
Overview
Its services are grouped into four areas: Managed Detection & Response (MDR), Infra & Cloud Security, Security Advisory and Identity Solutions. The company states it was founded in 2007 and serves more than 200 active customers. It has been ISO 27001 certified since 2022 and describes itself as vendor agnostic, working with partners including Palo Alto Networks, Microsoft Security, Google Security Operations, SentinelOne, Tenable, CyberArk and IBM. ACEN grew out of IS4U, an identity and access management firm that expanded into a broader cybersecurity offering. Within that leadership, Christophe Vereycken handled operations and Wouter Decruy financial strategy, while Jeffrey Van Vyve, who joined IS4U as sales manager, became Managing Partner responsible for sales and marketing in 2025. The company reports team growth of 20% per year and counted more than 100 people in July 2025. ACEN NV is registered under company number BE 1004.039.773. In February 2025 ACEN announced a partnership with Illumio for microsegmentation. ACEN MDR works with Google, SentinelOne and Silverfort. Reference customers include the Federaal Planbureau, for which ACEN delivers managed Microsoft 365 security and a 24/7 managed SOC.
Stated facts & numbers
- Founded: 2007
- Headquarters: Kontich (Antwerp)
- Employees: 51-200 (more than 100 in 2025)
- Customers: More than 200 active customers, including Federaal Planbureau
- Services: MDR, Infra & Cloud Security, Security Advisory, Identity Solutions
- Certification: ISO 27001 (2022)
- Company number: BE 1004.039.773
Key people
In the news
- We’re ready to 𝗸𝗶𝗰𝗸 𝘁𝗵𝗶𝗻𝗴𝘀 𝗼𝗳𝗳 next week at ACEN! Are you? 🤩 #JuniorMasterClass2026 #Cybersecurity
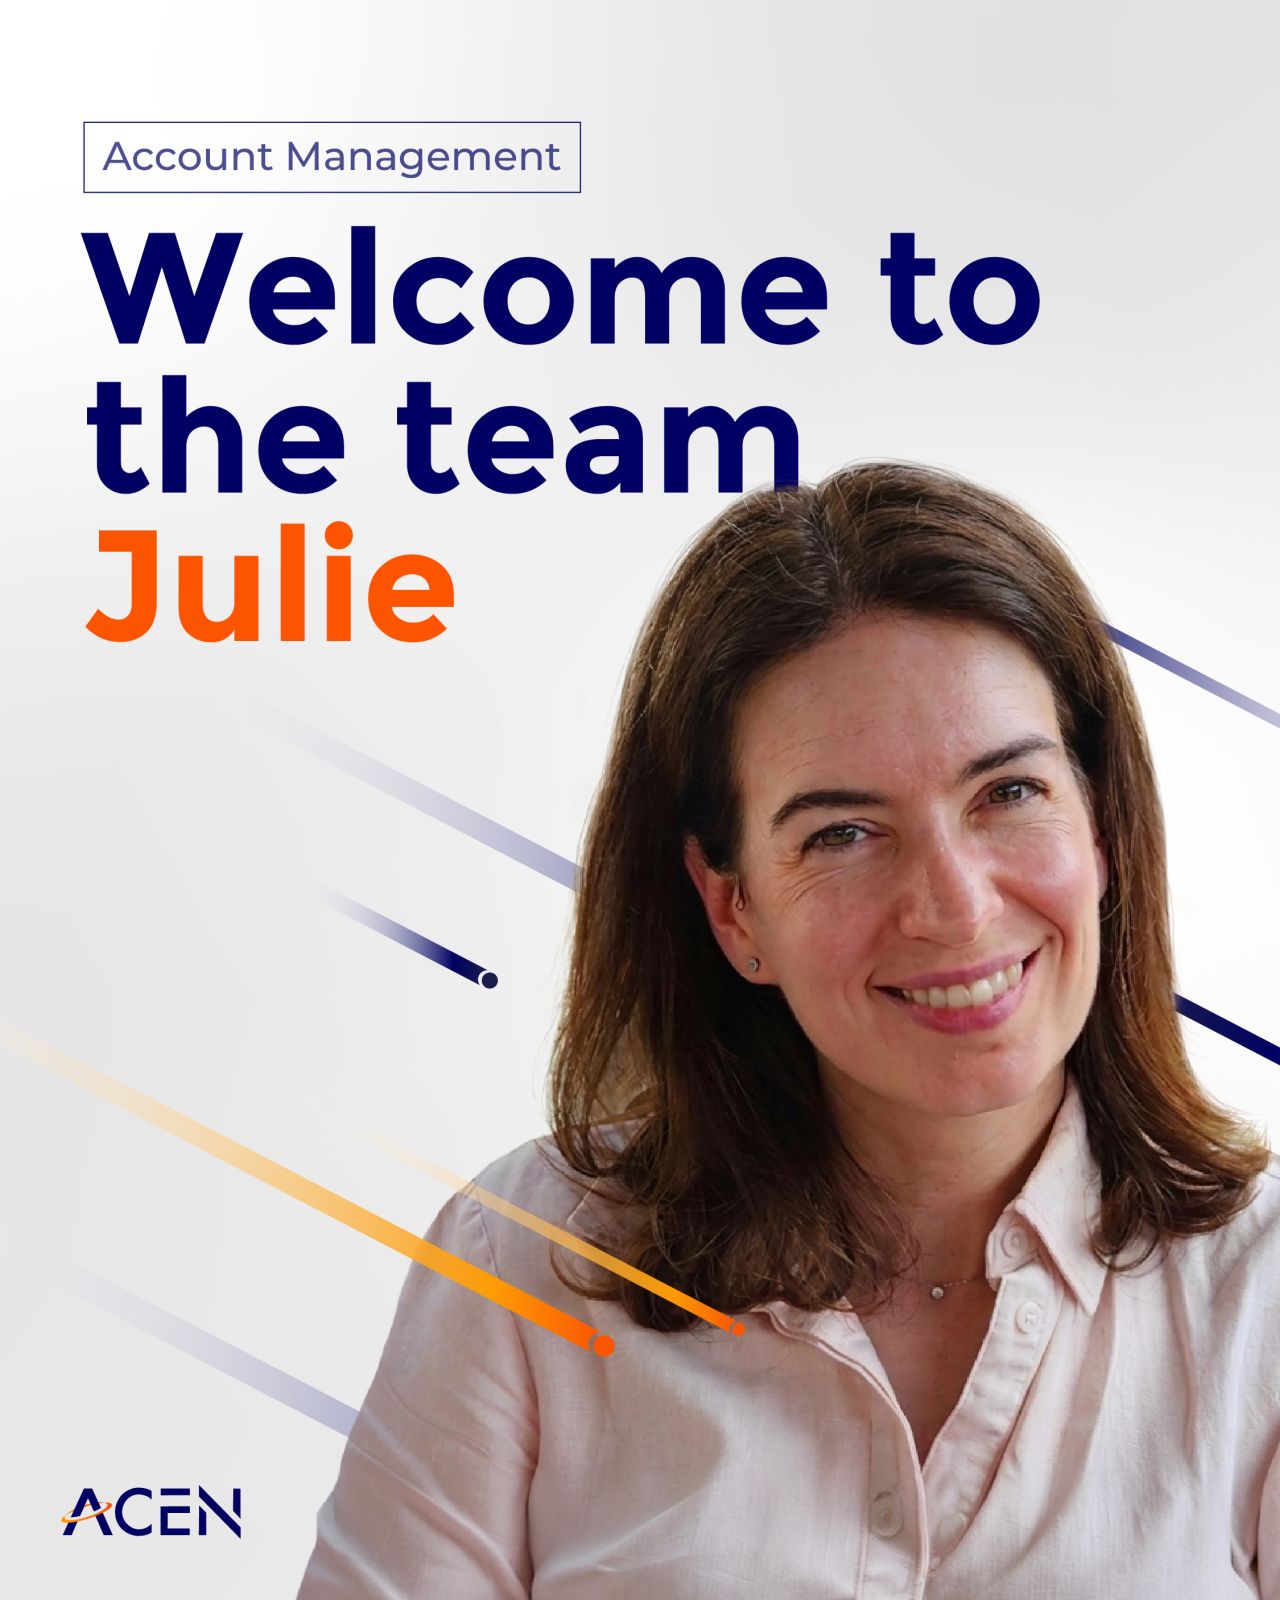
- We're happy to welcome Julie Bracke to the team! 🎉 She joins our business team as 𝗦𝗲𝗻𝗶𝗼𝗿 𝗔𝗰𝗰𝗼𝘂𝗻𝘁 𝗠𝗮𝗻𝗮𝗴𝗲𝗿. Julie combines a sharp, analytical approach with real client focus. And it shows in the results she delivers! Her 𝗲𝗻𝗴𝗮𝗴𝗲𝗺𝗲𝗻𝘁 and 𝗴𝗲𝗻𝘂𝗶𝗻𝗲 𝗶𝗻𝘃𝗲𝘀𝘁𝗺𝗲𝗻𝘁 in her clients create strong connections. Committed, loyal, and always 𝗿𝗲𝗮𝗱𝘆 𝘁𝗼 𝗴𝗼 𝘁𝗵𝗲 𝗲𝘅𝘁𝗿𝗮 𝗺𝗶𝗹𝗲. We consider Julie a true asset to any team, but of course we’re very happy to have her on ACEN’s. Are you
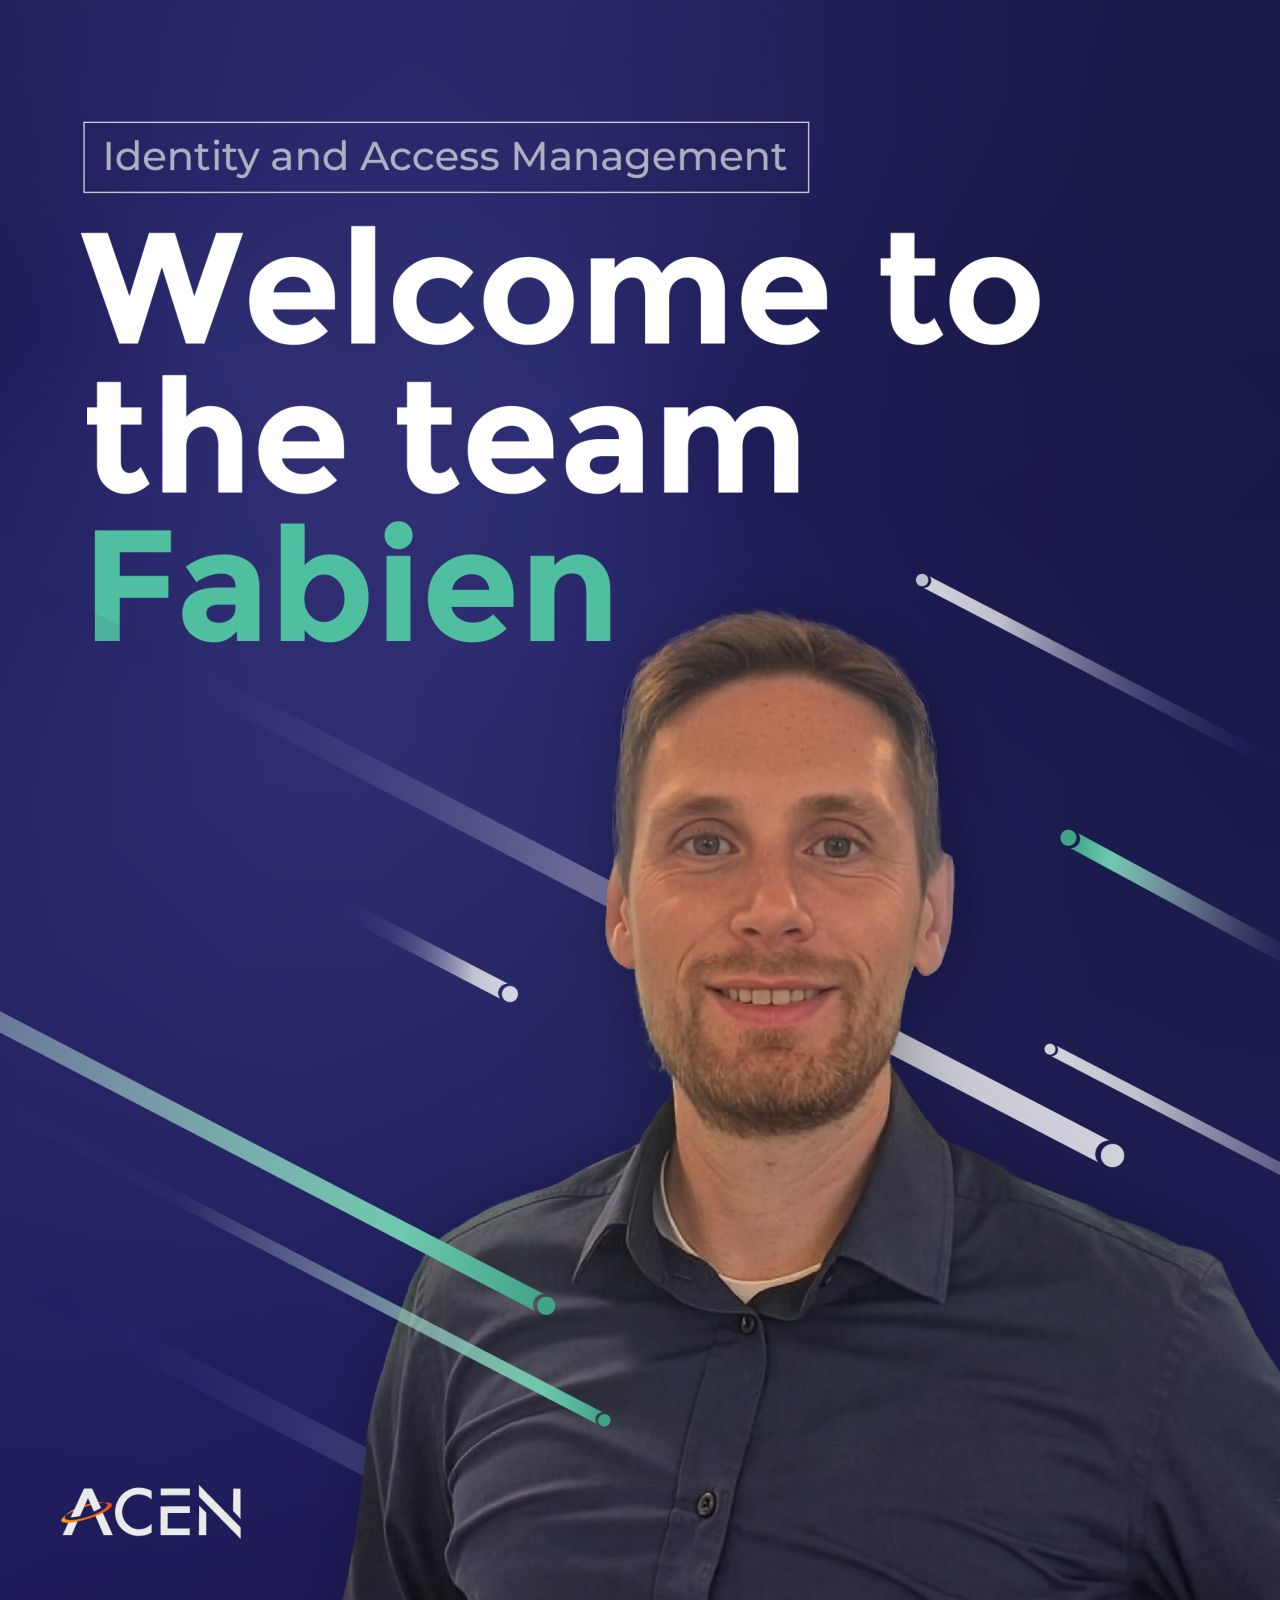
- We're happy to welcome Fabien D. to the team! 👏 He joins ACEN as 𝗜𝗱𝗲𝗻𝘁𝗶𝘁𝘆 & 𝗔𝗰𝗰𝗲𝘀𝘀 𝗠𝗮𝗻𝗮𝗴𝗲𝗺𝗲𝗻𝘁 (𝗜𝗔𝗠) 𝗕𝘂𝘀𝗶𝗻𝗲𝘀𝘀 𝗔𝗿𝗰𝗵𝗶𝘁𝗲𝗰𝘁. In his role, he will help organizations define their 𝗶𝗱𝗲𝗻𝘁𝗶𝘁𝘆, 𝗮𝗰𝗰𝗲𝘀𝘀 𝗴𝗼𝘃𝗲𝗿𝗻𝗮𝗻𝗰𝗲, 𝗿𝗼𝗹𝗲 𝗺𝗮𝗻𝗮𝗴𝗲𝗺𝗲𝗻𝘁, 𝗮𝗻𝗱 𝗰𝗼𝗺𝗽𝗹𝗶𝗮𝗻𝗰𝗲 𝗻𝗲𝗲𝗱𝘀. One of his key strengths is translating business and security requirements into sustainable #IAM strategies, governance models and operating frameworks. Fabien has led large-scale IAM
- We have some exciting news to share! 👇 👇 👇 ACEN is developing 𝗕𝗲𝗹𝗴𝗶𝘂𝗺’𝘀 𝗳𝗶𝗿𝘀𝘁 𝗢𝗖𝗮𝗮𝗦 (𝗢𝗽𝗲𝗻 𝗦𝗼𝘂𝗿𝗰𝗲 𝗖𝘆𝗯𝗲𝗿𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆-𝗮𝘀-𝗮-𝗦𝗲𝗿𝘃𝗶𝗰𝗲) 𝗽𝗹𝗮𝘁𝗳𝗼𝗿𝗺, with the support of VLAIO, Flanders' Agency for Innovation and Entrepreneurship. The platform addresses a 𝗰𝗵𝗮𝗹𝗹𝗲𝗻𝗴𝗲 many organizations are facing today: 𝗱𝗶𝗴𝗶𝘁𝗮𝗹 𝘀𝗼𝘃𝗲𝗿𝗲𝗶𝗴𝗻𝘁𝘆. In June 2026, the 𝗘𝘂𝗿𝗼𝗽𝗲𝗮𝗻 𝗖𝗼𝗺𝗺𝗶𝘀𝘀𝗶𝗼𝗻 introduced new measures to 𝗿𝗲𝗱𝘂𝗰𝗲 𝗱𝗲𝗽𝗲𝗻𝗱𝗲𝗻𝗰𝗲 𝗼𝗻
- A month has passed since the 𝗗𝘂𝘁𝗰𝗵 𝗖𝘆𝗯𝗲𝗿𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗔𝗰𝘁 (#𝗖𝘆𝗯𝗲𝗿𝗯𝗲𝘃𝗲𝗶𝗹𝗶𝗴𝗶𝗻𝗴𝘀𝘄𝗲𝘁) officially came into effect. Around 8.000 Dutch organizations have to comply with the national implementation of the 𝗡𝗜𝗦𝟮 𝗱𝗶𝗿𝗲𝗰𝘁𝗶𝘃𝗲. Meaning stricter requirements around risk management, reporting, and accountability. 𝗕𝘂𝘁 𝗰𝗼𝗺𝗽𝗹𝗶𝗮𝗻𝗰𝗲 𝗶𝘀 𝗮𝗯𝗼𝘂𝘁 𝗺𝗼𝗿𝗲 𝘁𝗵𝗮𝗻 𝗽𝗿𝗲𝗽𝗮𝗿𝗶𝗻𝗴 𝗳𝗼𝗿 𝗮𝗻 𝗮𝘂𝗱𝗶𝘁. ✅❌ Good reports, shiny certificates and checked boxes don’t necessarily
- We're #hiring a new Project Manager in Kontich, Flemish Region. Apply today or share this post with your network.
- 𝗗𝗶𝗱 𝘆𝗼𝘂 𝗽𝗮𝘂𝘀𝗲 𝘆𝗼𝘂𝗿 𝘀𝗰𝗿𝗼𝗹𝗹𝗶𝗻𝗴 𝘁𝗼 𝗿𝗲𝗮𝗱 𝘁𝗵𝗶𝘀? ⏸️ Normally, we'd advise against standing still. But this time, we'll allow it. Because we'd like to talk about one of our core values: 𝗧𝗵𝗶𝗻𝗸 𝗳𝗼𝗿𝘄𝗮𝗿𝗱. 𝗖𝘆𝗯𝗲𝗿𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗻𝗲𝘃𝗲𝗿 𝘀𝘁𝗮𝗻𝗱𝘀 𝘀𝘁𝗶𝗹𝗹. ➡️New threats emerge every day. ➡️Technologies evolve. ➡️Attackers adapt. 𝗟𝘂𝗰𝗸𝗶𝗹𝘆, 𝗻𝗲𝗶𝘁𝗵𝗲𝗿 𝗱𝗼 𝘄𝗲. At ACEN, we always encourage our people to challenge assumptions, explore new technologies, and keep expanding
- Your architecture is built on it, yet 𝘆𝗼𝘂 𝗰𝗮𝗻’𝘁 𝗮𝗹𝘄𝗮𝘆𝘀 𝘁𝗿𝘂𝘀𝘁 𝗶𝘁. Ra Ra, what is it? 🤷 We’re talking about 𝗰𝗼𝗱𝗲. 𝗔𝗿𝗲 𝘆𝗼𝘂 𝘀𝘂𝗿𝗲 𝘆𝗼𝘂 𝗰𝗮𝗻 𝗳𝘂𝗹𝗹𝘆 𝘁𝗿𝘂𝘀𝘁 𝘁𝗵𝗲 𝗰𝗼𝗱𝗲 𝘁𝗵𝗮𝘁’𝘀 𝗿𝘂𝗻𝗻𝗶𝗻𝗴 𝗶𝗻 𝘆𝗼𝘂𝗿 𝗲𝗻𝘃𝗶𝗿𝗼𝗻𝗺𝗲𝗻𝘁? 𝗜𝘀 𝗶𝘁 𝘁𝗿𝘂𝗹𝘆 𝘄𝗵𝗮𝘁 𝗶𝘁 𝗰𝗹𝗮𝗶𝗺𝘀 𝘁𝗼 𝗯𝗲? If you are doubtful about the answers, then you might have just uncovered a 𝗯𝗹𝗶𝗻𝗱 𝘀𝗽𝗼𝘁 in your security strategy. 👁️👁️ We notice an increased amount of attacks on software supply chains and

Something wrong or missing? Send an update. Fixed within 24 hours.