
Overview
Approach Cyber is a cybersecurity and privacy partner that helps organizations manage cyber resilience while they focus on their business. The company combines strategic advice, offensive and defensive expertise, SOC operations, and product engineering through its AXS Guard managed security platform, offering services including phishing awareness, governance and risk compliance, ethical hacking, threat detection and response, and cloud security.
Org chart
In the news
- Rendez-nous visite lors du Digital Wallonia Cyber Forum 2026, le 29 septembre 2026 à l'Aula Magna (Louvain-la-Neuve), le rendez-vous incontournable de la cybersécurité en Wallonie ! 📍 Venez nous rencontrer sur notre stand ou suivez l'intervention de David Vanderoost à 13h30, dans le panel consacré aux SOC mutualisés et à leur adaptation aux différentes entités et secteurs. 👉 L'inscription est gratuite : https://lnkd.in/ePBHnFwv Au plaisir de vous y voir!!!
- Compliant zijn is niet genoeg. De juiste technologie in huis hebben ook niet." Cyberdreigingen en regelgeving evolueren sneller dan ooit, maar hoe zorg jij er dan als lokaal bestuur voor dat je écht digitaal weerbaar wordt? Tijdens de CIS Dag van V-ICT-OR | VLAAMSE ICT ORGANISATIE op 1 oktober duikt onze Head of Sales, Dan Verbruggen, dieper in dit thema. In zijn breakout-sessie neemt hij je mee in de realiteit van 'echte' cyber resilience vandaag. 🗣️ Dan Verbruggen (Head of Sales bij Approach Cyber) 💬 Cyber resilience: de

- Cybersecurity bij steden, gemeenten en openbare besturen: hoe voorbereid is jouw organisatie op de uitdagingen van morgen? 💁 Op 1 oktober is Approach Cyber aanwezig op de CIS Dag van V-ICT-OR | VLAAMSE ICT ORGANISATIE in Mechelen. We verwelkomen je graag bij onze stand voor een vrijblijvend gesprek over wat wij dagelijks zien in jullie werkveld of gewoon voor een korte babbel! 📅 Datum: Donderdag 1 oktober 2026 ⏰ Tijd: 09:00 – 17:00 📍 Locatie: Lamot Congres- en Erfgoedcentrum, Mechelen 👥 Voor wie: IT-verantwoordelijken, CISO's,
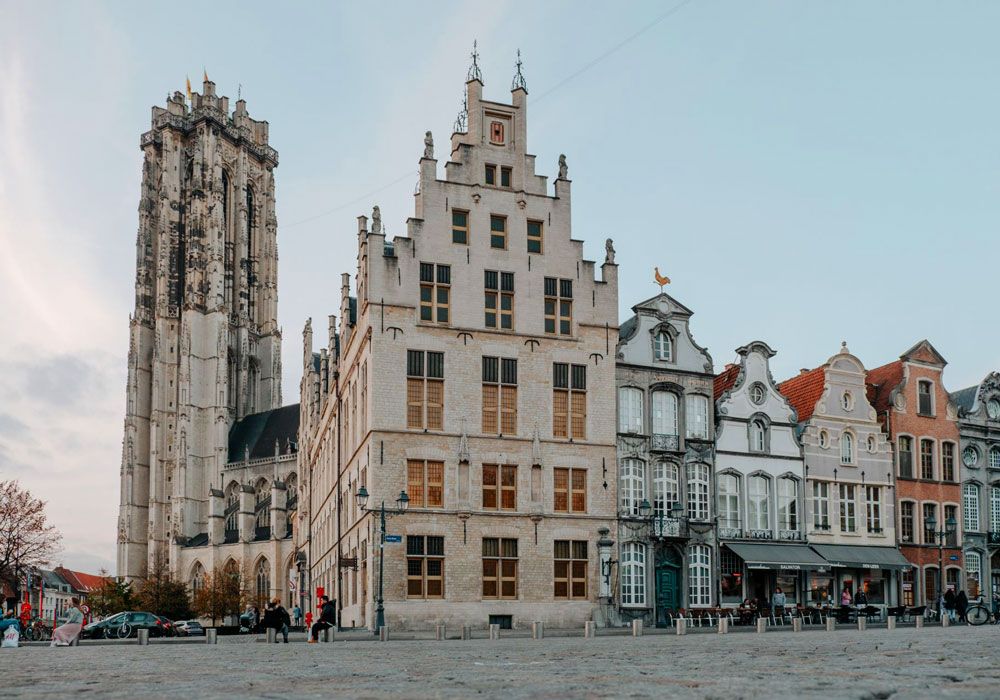
- 1 oktober is het reeds zover [CIS] cyber en informatieveiligheid dag 2026 - WELKOM - Lamot Mechelen [CIS] cyber en informatieveiligheid dag 2026. Deze jaarlijkse V-ICT-OR kennisdag (10de editie) biedt een uniek platform voor het delen van kennis en ervaringen over de nieuwste trends en uitdagingen op het gebied van privacy, cyberbeveiliging en informatiemanagement. Thema van deze editie = Beyond Compliance - From NIS2 to Digital Resilience - wij gaan verder 🗲 Versterk je cyberweerbaarheid. 🗲 Bescherm jouw organisatie en
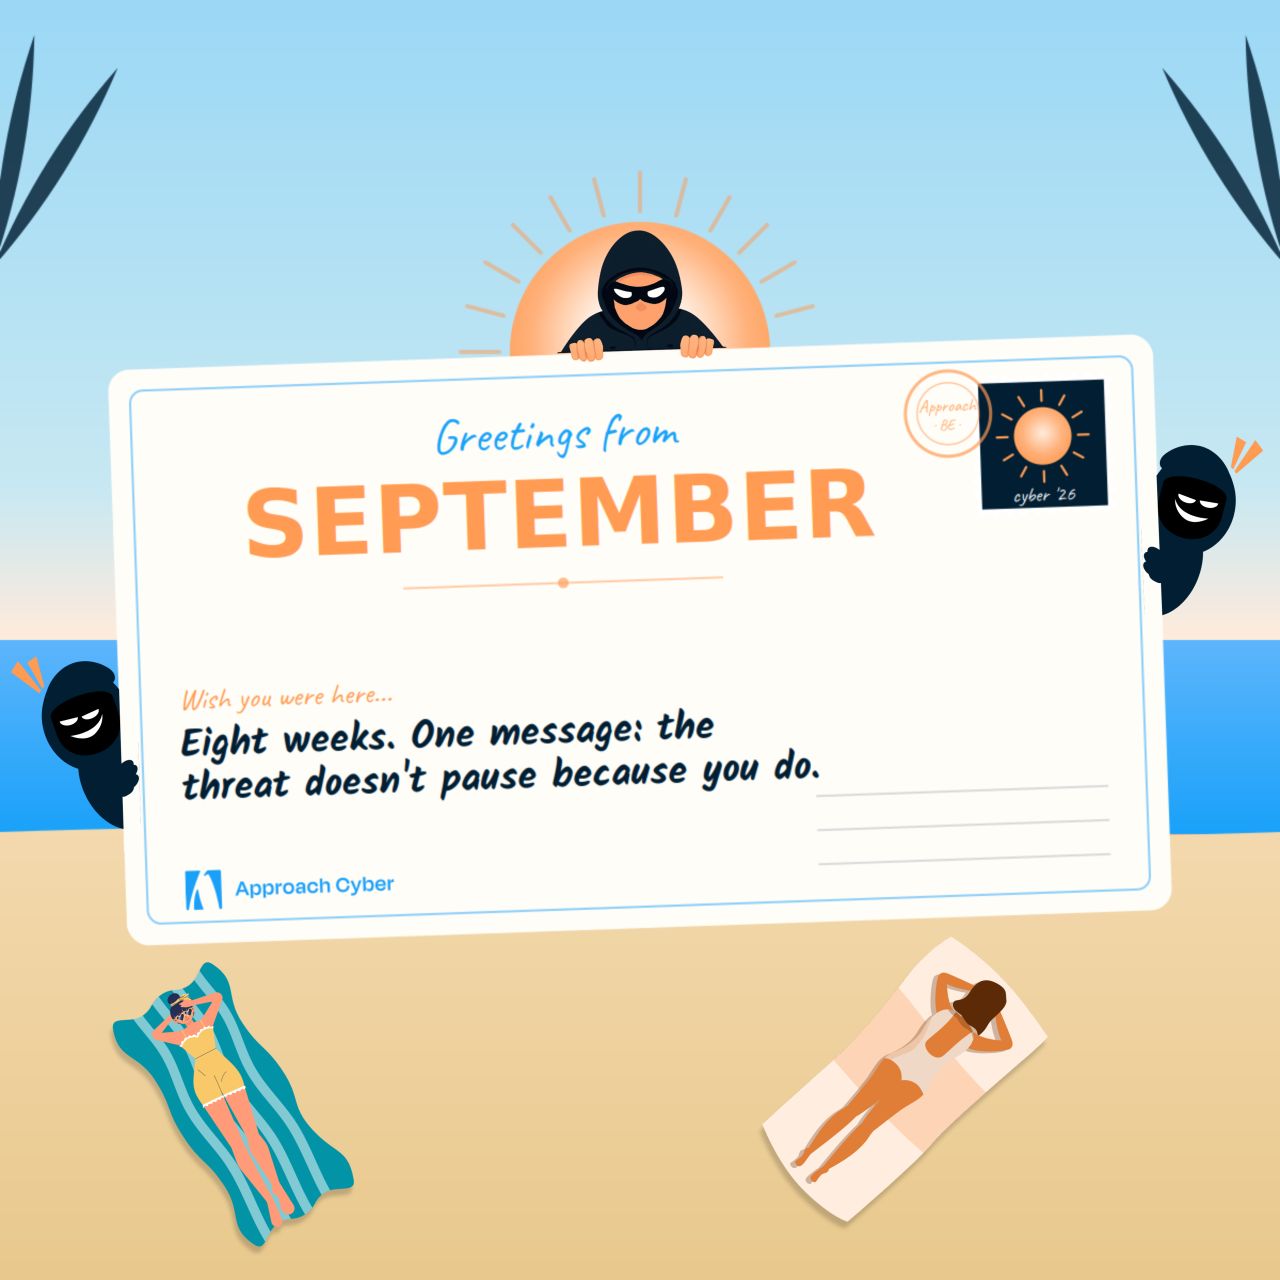
- Eight weeks. One message: the threat doesn't pause because you do. September brings its own risks; full inboxes, deferred decisions, distracted teams. The window doesn't close; it shifts. 🗣️ 💬 If this series raised a question you haven't answered yet, now is a good time. Specific need, no idea where to start, or just want a conversation? We're here. No pitch, no pressure. 👉 https://loom.ly/spXcqM4 #cyberresilience #safeholidays #approachcyber #cybersecurity
- OpenAI and Anthropic are right to be scared: The next innovations in the agentic AI space are not in the models, they're in the harnesses. I was invited to talk at Approach Cyber yesterday (thank you David Vanderoost!) and I got to share more about this exact point. Better models do yield improvements, but better harnesses are where the next magnitudes of improvements are unlocked. And you know what, all those billions of dollars invested in model training got us there. The frontier labs are utility providers, competing against open
- Our pentesters got in. Again. 🚨🥷 5th edition of the Approach Cyber Pentest Annual Report is out. The findings across Belgian organisations are consistent: misconfigurations, weak credentials, unpatched systems, overprivileged accounts. Not exotic. Not new. Just unaddressed. If you're building a security roadmap or presenting risk to a board 👉 this is your benchmark. 📥 https://loom.ly/bOvVeRU #pentestreport #safeholidays #redteam #cyberresilience #approachcyber
- Threat modelling is no longer optional. NIS2 and the CRA have made risk assessment in software development a legal requirement; ✅ Documentation ✅ Risk registers ✅ Evidence of security decisions at design stage ✅ A repeatable methodology. Most development teams have gaps they don't know about. 👇 Our publication maps exactly what's required and where teams typically fall short 👇 https://loom.ly/aBZw2o0 #threatmodelling #securedevelopment #appsec #nis2 #cyberresilienceact #safeholidays

Something wrong or missing? Send an update. Fixed within 24 hours.