
Overview
Ceeyu's SaaS platform identifies vulnerabilities and risks across supply chains through automated scans, data lookups, and digital questionnaire-based assessments. The platform combines questionnaires covering cybersecurity, financial, ESG, and compliance risks with objective, real-time attack surface scanning insights. Suppliers have access to their assessment results to address identified issues proactively.
In the news
- More soon
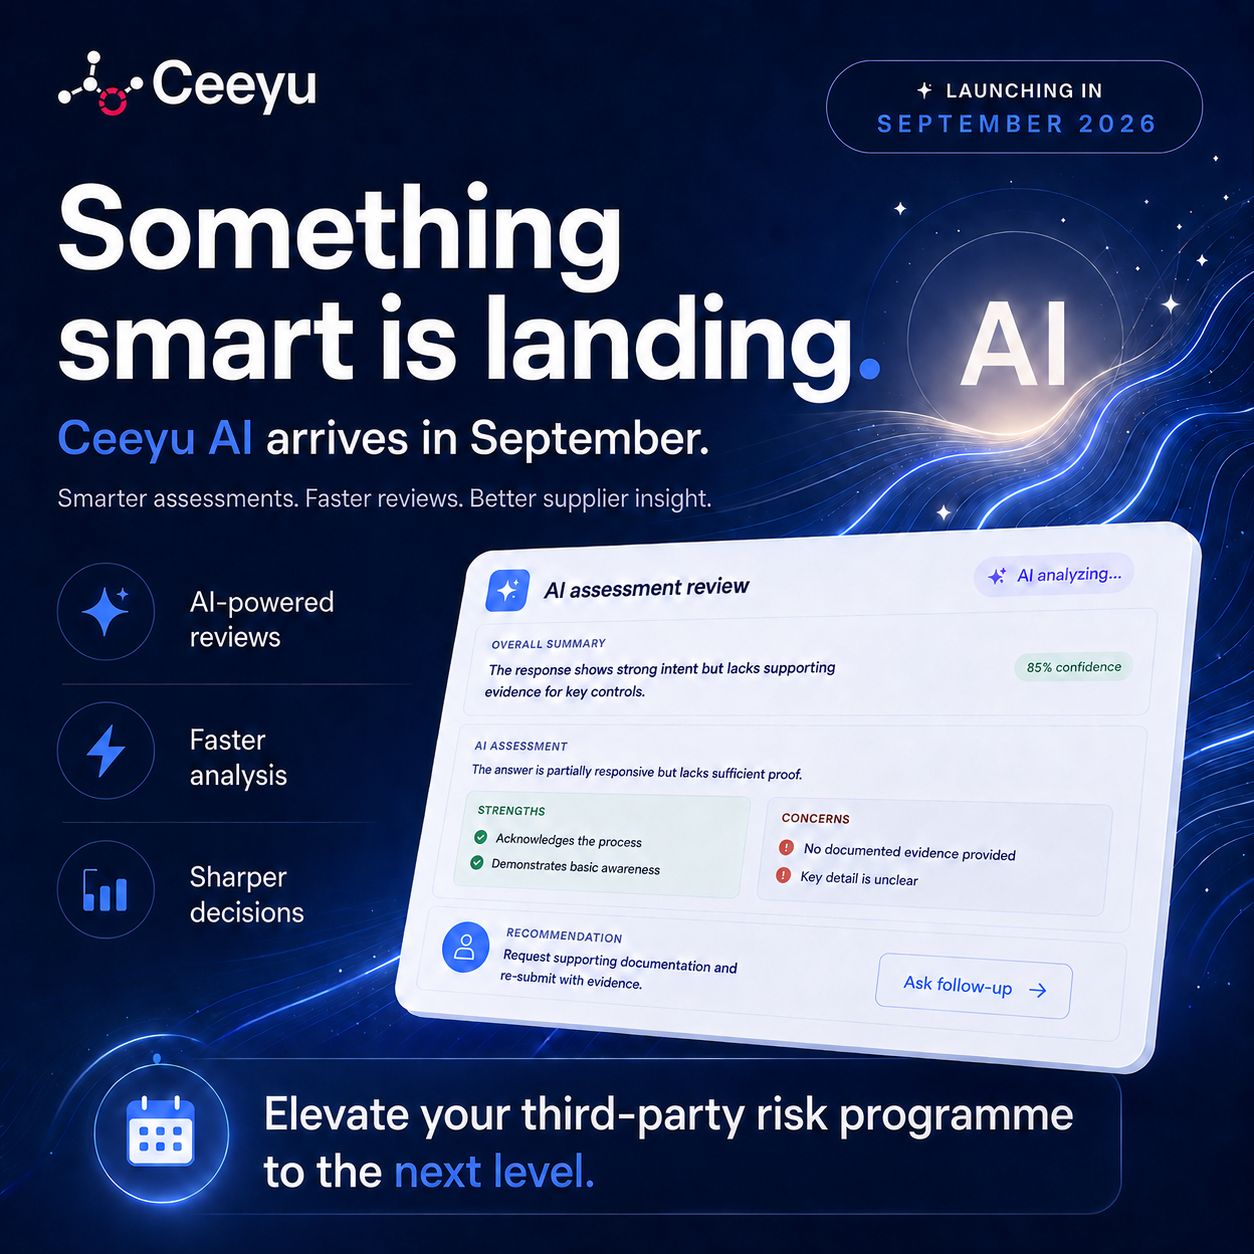
- Too many teams learn that a supplier was breached the same way everyone else does: from a post online. By the time it reaches your feed, it is already your problem. It does not have to work that way. Ceeyu combines two things: continuous monitoring of your suppliers' external security posture, and breach monitoring. So a new exposure, or a supplier that just surfaced in a breach, reaches you as an early signal instead of a headline.
- NIS2 and DORA both expect you to keep a supplier risk register, and to actually keep it current. For most teams that still lives in a spreadsheet nobody quite trusts. Ceeyu gives you the register out of the box: every supplier, their criticality, their attack surface score, their assessments, whether they have shared their security posture through a Trust Center, and more. One live view, instead of a document that ages the moment you save it.
- Suppliers are tired of answering the same security questionnaire for the fortieth customer. Buyers are tired of chasing them for a PDF that is already out of date. The Ceeyu Trust Center fixes both, and it is free for everyone. Suppliers maintain their posture once and share it live. Buyers get a current view instead of chasing. Publish on Ceeyu's domain or your own.

Related profiles
Something wrong or missing? Send an update. Fixed within 24 hours.