
Overview
Cingulum offers cybersecurity governance and compliance solutions including cybermaturity assessment, risk assessment, NIS2 management, internal and external audits, and CISO-as-a-Service. The company provides practical cybersecurity support for SMEs with up to 50% funding available through VLAIO, and helps organizations meet ISO 27001, NIS2, and Cyber Resilience Act requirements.
Leadership & org chart
In the news
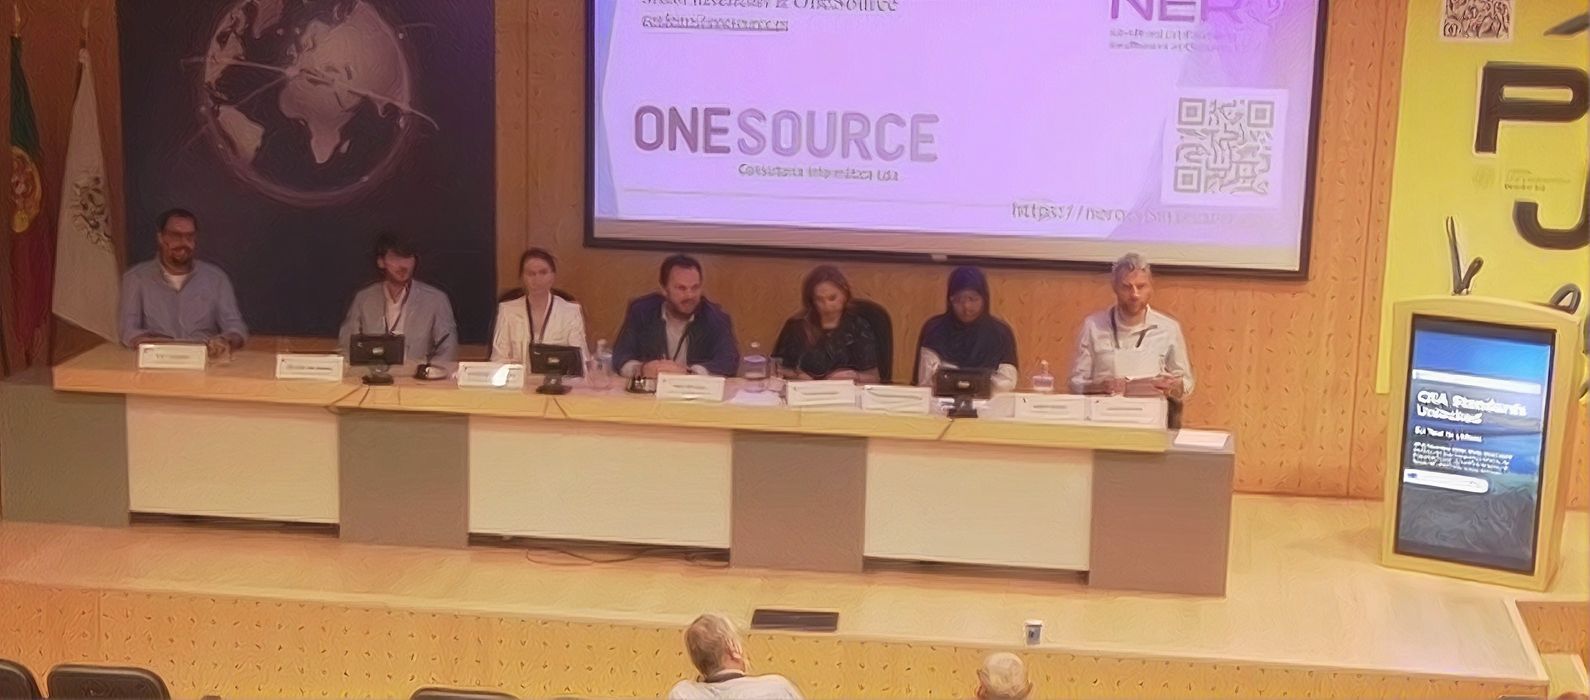
- A day packed with Cyber Resilience Act (CRA) activity across Europe! It has been a busy day for Refracted on the CRA front with activity spanning multiple European initiatives and communities. Our esteemed CEO Ben Van Erck was present at the CRA Unlock Tour in Lisbon, connecting with stakeholders and exchanging perspectives on the implementation of the Cyber Resilience Act. Meanwhile, our colleague Siebe De Roovere joined our partners at CRANIUM and Cingulum for a dedicated webinar on the CRA, bringing together several essential
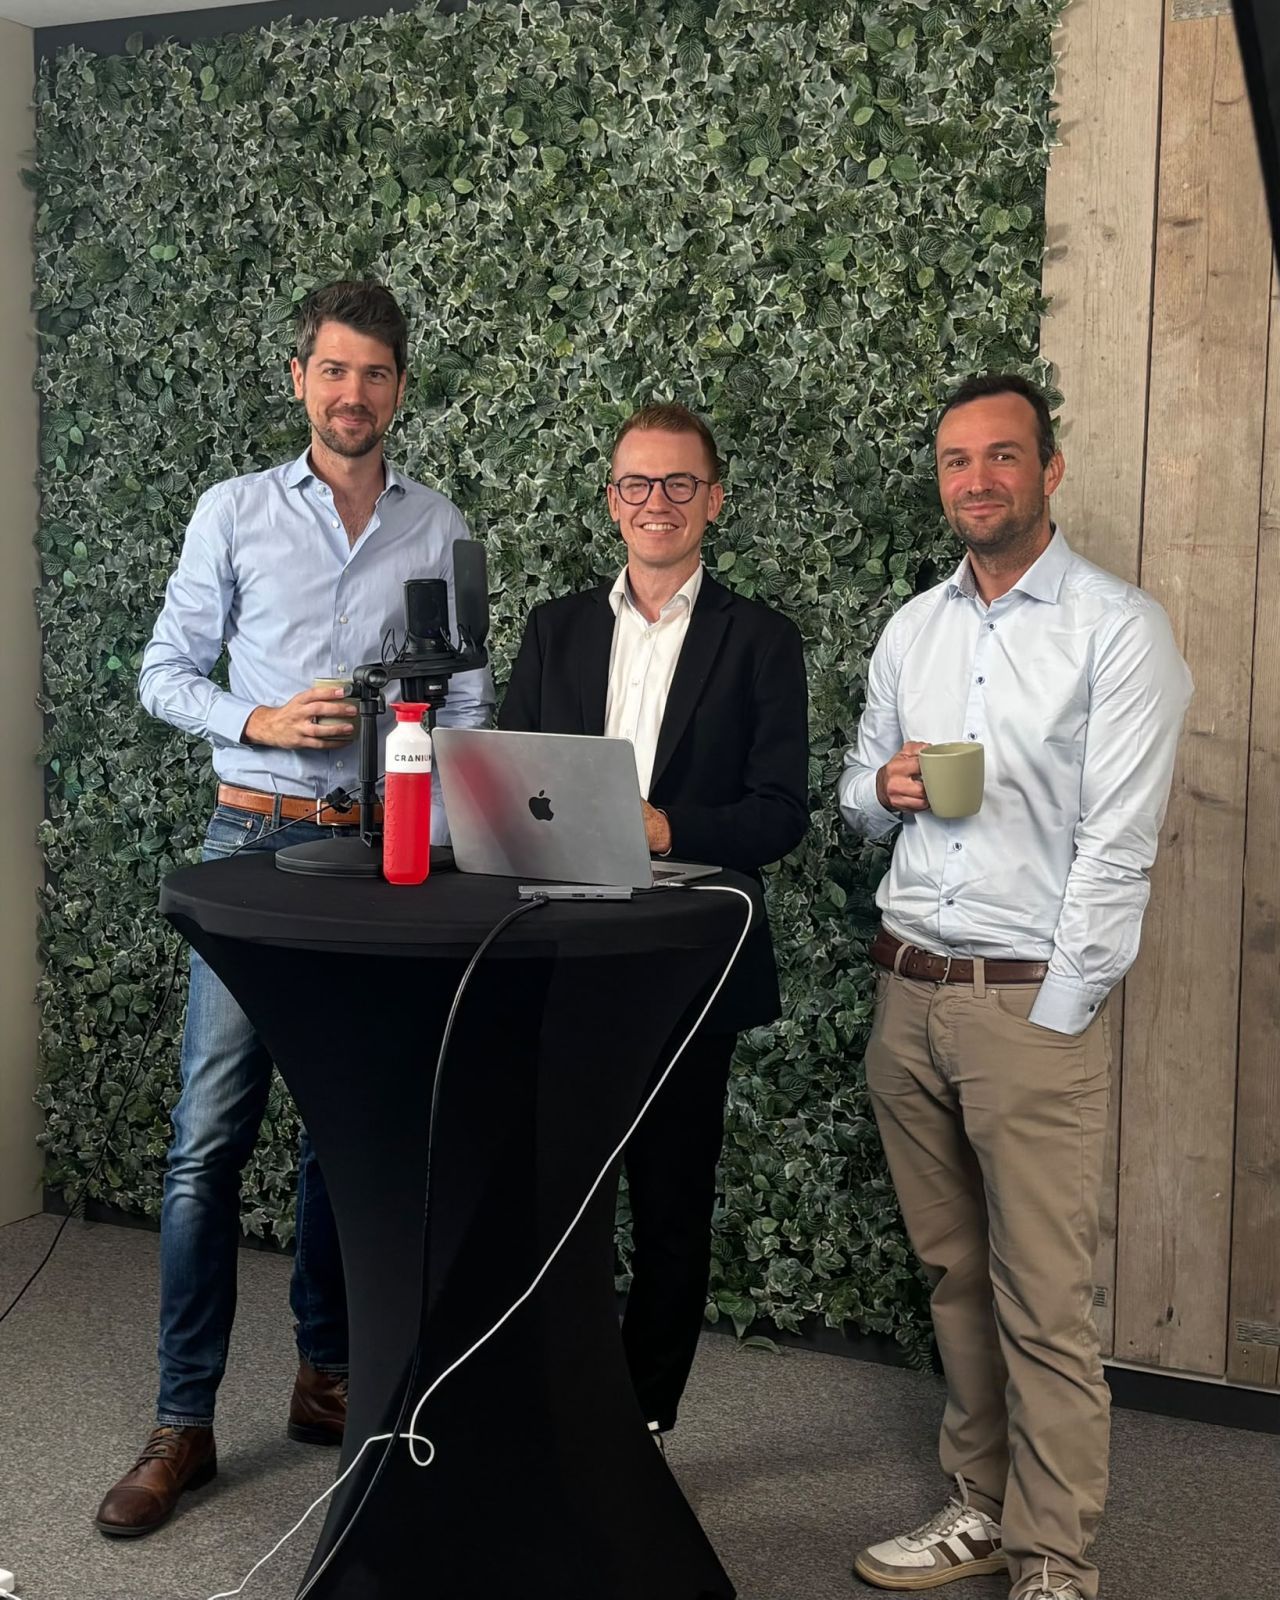
- Last call 🚨 Schrijf je nog snel in! Tijd om mee te zijn met de Cyber Resilience Act. Morgen leggen we het uit, samen met Cingulum en Refracted Security. Zit je met vragen over de CRA? Je kan ze morgen stellen. 👩💻 17 september, 13u-14u 🔗 https://loom.ly/3fse4sI Kan je niet live volgen? Schrijf je toch in en ontvang achteraf de opname en de slides.
- Every product company will eventually get that email: "I found something in your product." What happens next is not a technical question. It's an organisational one. Who receives it, who decides how bad it is, who talks to the customer, and who signs off on the timeline. The CRA turns that from good practice into a legal obligation: vulnerability handling, SBOM, coordinated disclosure, and notification to ENISA within 24 and 72 hours. Core requirements apply from December 2027. We build that capability with product teams from an
- Nog 7 dagen tot onze webinar over de Cyber Resilience Act. Even testen: Kun je vandaag onmiddellijk antwoorden op deze vragen? ❓ Wie ontvangt een kwetsbaarheidsmelding? ❓ Wie beslist of ze meldingsplichtig is? ❓ Wie contacteert de betrokken stakeholders? ❓ Kun je binnen 24 uur rapporteren? Twijfel je bij één van deze vragen? Dan is deze sessie voor jou. Registreer je hier: https://loom.ly/NYE29FU 📅 17 september 🕐 13.00 - 14.00 uur 🎟️ Gratis webinar
- As of 11 September, the reporting obligations under the Cyber Resilience Act apply. By the end of 2027, your organisation needs to be fully in order. Together with CRANIUM and Cingulum, we'll walk you through the key changes in one hour: what falls in scope, how to set up vulnerability management, SBOM handling and coordinated disclosure for the 24 and 72 hour reporting window, and which demonstrable artefacts supervisors actually expect. Complex regulation, brought back to what it practically means for your products. Free webinar on
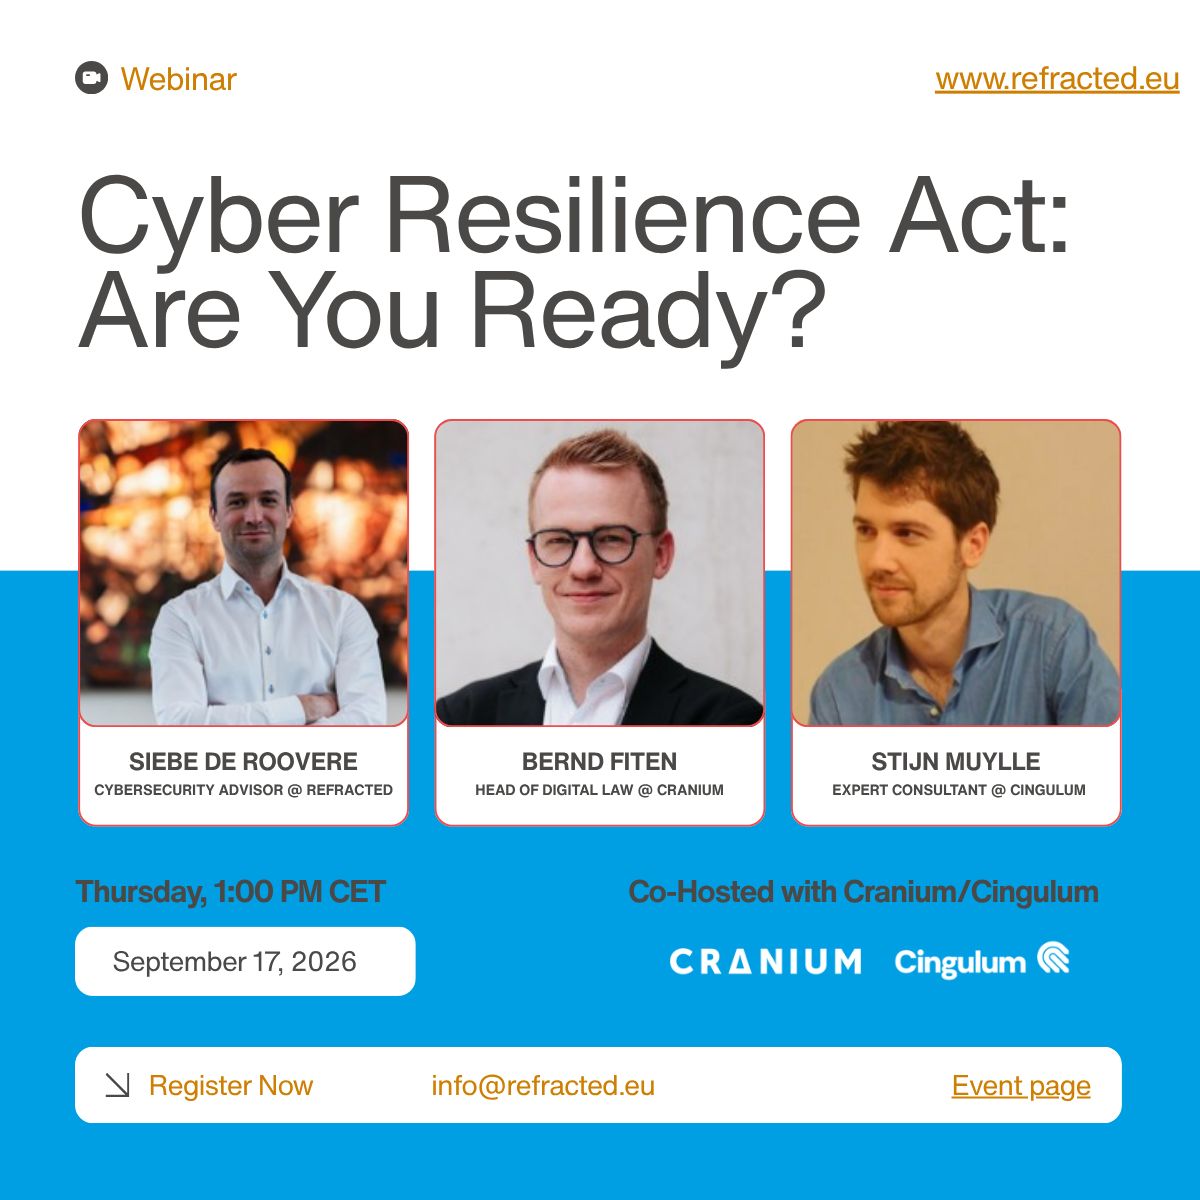
- Verkoop je digitale producten en hoor je het donderen in Keulen bij CRA? Dan is onze volgende webinar wellicht voor jou! Vanaf 11 september gaat de Cyber Resilience Act in voegen en moet ook jij eraan voldoen als je digitale producten verkoopt binnen de EU. Wil je graag bijleren over de impact op juridisch, technisch en governance-vlak? Onze expert Bernd Fiten , en collega's Stijn Muylle (Cingulum) & Siebe De Roovere (Refracted Security) nemen je mee in het volledige verhaal. 👉🏽 Schrijf je nu in voor onze webinar op 17 september om
- De Cyber Resilience Act legt strikte deadlines op wanneer een kwetsbaarheid in een product wordt ontdekt. Maar hoe weet je of jouw organisatie er klaar voor is? Loop onderstaande checklist eens door: ☐ We weten wie kwetsbaarheidsmeldingen ontvangt. ☐ We hebben duidelijk vastgelegd wie beslist of een incident meldingsplichtig is. ☐ We kunnen snel bepalen welke producten, versies en klanten impact ondervinden. ☐ Onze escalatiepaden zijn getest en niet alleen gedocumenteerd. ☐ Juridische, technische en
- The CRA's reporting obligations go live on 11th of September. Six days later, we're getting into what that looks like in practice, together with CRANIUM (legal) and Cingulum (technical & organizational). In 𝗼𝗻𝗲 𝗵𝗼𝘂𝗿, you'll walk away knowing: • Which of your products with digital elements fall under the CRA, and what that means technically • How to set up vulnerability management, SBOM handling and coordinated disclosure so a 24/72-hour report is actually possible • Why a policy document isn't enough, so what auditors actually

Something wrong or missing? Send an update. Fixed within 24 hours.