
Overview
Codific is a secure software development company that builds HR-Tech, Ed-Tech, and Medtech collaboration tools leveraging security by design and privacy by design principles.
Key people
In the news
- Marathon or sprint? There are two ways to run a #SAMM assessment. 🏃 One option is a full-day workshop. The other is five 90-minute sessions. Which one works better depends on your team, and it’s only the first of many choices that shape how an assessment turns out. Aram H. from CODIFIC and Maxim Baele from Toreon sat down for a 40-minute session on how they run SAMM assessments in practice, based on assessments across organisations of every shape. They cover: ➡️ Who needs to be in the room, business function by business
- One week until OWASP® Foundation Global AppSec USA 🌉 There’s plenty on the agenda we’re looking forward to. Sebastien Deleersnyder and Rob van der Veer are both on the programme, and we’re looking forward to catching their sessions. On November 4 we have the #SAMM User Day, focused on SAMM in the age of the AI SDLC. Aram H. is speaking on SAMM in the Age of Agentic AI, Dag Flachet on the rise of PRC, and Brian Glas is sharing the latest SAMM Benchmark updates. We’re also looking forward to hearing Nariman Aga-Tagiyev and Max
- Our next #SAMMY Community Call is on Tuesday, November 17, and this one is all about risk. 🎯 We’re walking through a set of new features, live: → Product risk assessment, with risk scenarios, mitigating control management, and an assisted threat modeling approach → A new CRA scope assessment tool, plus real CRA use cases → Supplier risk assessment → MCP, with a threat modeling skill → Multi-lingual support 🌍 We’ll also open up the #roadmap, and leave time for your questions and feature requests. 💬 🗓️ Tuesday, November
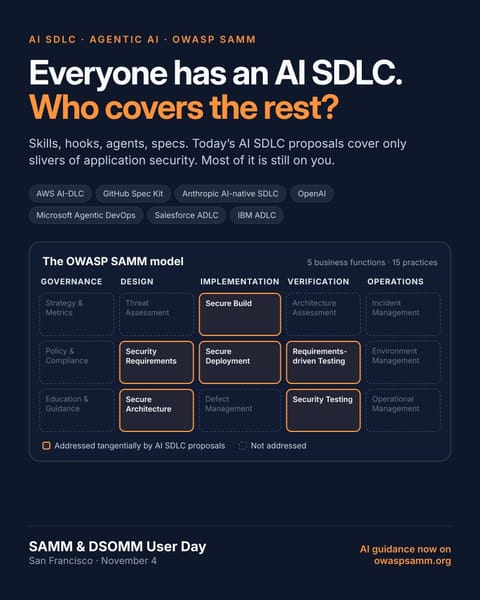
- Is #SAMM still relevant when AI agents write the code? 🤖 It’s a question the SAMM community is hearing more and more. AI is changing not only what software teams build, but how quickly and autonomously they design, generate, test, deploy and maintain it. That’s the focus of the SAMM User Day at OWASP® Foundation Global AppSec USA in San Francisco on November 4: SAMM in the age of the AI SDLC. 🎤 There are several talks on the topic, including the SAMM core team’s perspective on what changes and an overview of the new AI guidance
- What’s cooking in #SAMMY? Here’s a teaser of what we’ve been building. We’re constantly working behind the scenes to make SAMMY smarter, faster, and more seamless for your security and compliance workflows. Here is a brief look at a few powerful updates rolling out: 🔍 Expanded data access & #MCP integration We're expanded Model Context Protocol (MCP) access across SAMMY - your AI tools will be able to seamlessly fetch supplier assessment data and contextual information directly through the expanded API, making data extraction
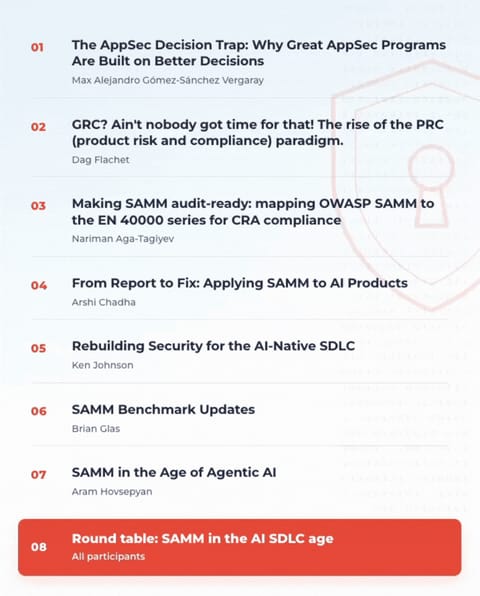
- The #SAMM User Day line-up is taking shape. 🎤 San Francisco, November 4. The day runs alongside OWASP® Foundation Global AppSec USA, and three of our team are on the agenda: ➡️ Aram H. on SAMM in the age of agentic AI ➡️ Dag Flachet on the rise of PRC, and why GRC struggles to keep up with software products ➡️ Brian Glas with the latest SAMM Benchmark updates They're joined by practitioners from the community. Max Alejandro G. looks at why great AppSec programmes are built on better decisions, and Nariman Aga-Tagiyev covers
- Four sessions. One security expert. One CRA lawyer. Aram H. and Lara Brito have been breaking down the Cyber Resilience Act the way engineering teams actually need to hear it - through real examples, not abstractions. 🎙️ The series covers: → What counts as a "product with digital elements," and the three product risk categories → Risk assessment using the FAIR methodology — and why "we answered all the checklist items" isn't compliance → The technical requirements behind security by design and security by default → Why
- San Francisco. November 4. A full day with the #SAMM & #DSOMM community. The User Day runs alongside OWASP® Foundation Global AppSec USA, bringing together practitioners actually using these frameworks, not just talking about them in theory. 💭 Expect talks on real assessments, roadmaps, and the lessons that came out of them, plus space to connect with others working through the same challenges you are. If you're already heading to AppSec USA, this is worth building into your schedule. 📆 🔗 Registration details here:

Alumni 1 went on to found or lead
 Dag FlachetInvestor and Partner→Founder and Managing Partner at Flachet Holdings NV
Something wrong or missing? Send an update. Fixed within 24 hours.