
Overview
Founded by Stijn Jans and headquartered in Schelle near Antwerp, Intigriti operates one of Europe's leading bug bounty and responsible disclosure platforms. Companies run programs on the platform to invite vetted security researchers to find vulnerabilities in their systems, with rewards paid for validated findings.
The bug bounty model supplements traditional penetration testing with continuous, crowd-sourced security testing at scale. Intigriti manages the coordination layer: researcher onboarding, vulnerability triage, reward distribution, and compliance documentation.
With 100+ employees, Intigriti has established itself as a major player in the European Cybersecurity market and competes with HackerOne and Bugcrowd for enterprise bug bounty programs.
Funding & milestones
2 events found for Intigriti · 2020–2022
Series AVenture / equity1 source€4.14M
Reported amount €4,140,000
Company reports €4.14m Series A, led by ETF Partners.
InvestorsETF PartnersSeries BVenture / equity1 source€21.13M
Reported amount €21,133,700
Company reports €21,133,700 Series B; redundant word 'million' after the numeric figure in the release is a typographical error, consistent with the €21M headline.
Recorded history so far. Original currencies are preserved; amounts in different currencies are not added together. Debt, grants, acquisitions and listings are separate event types. Undated events appear last.
Leadership & org chart
In the news
- The SANS Difference Makers Awards recognize cybersecurity professionals who go above and beyond, including practitioners, educators, researchers, and community builders whose work quietly helps shape the field. Congratulations to our colleague Chris Holt, our Strategic Engagement & Community Architect, who has been named a finalist as part of the OWASP OASIS team for the 2026 SANS Difference Makers Awards for Innovation of the Year. If secure open source and community matters to you, please take a minute to vote for
- INTI’S HACKING TALK IS NOW OUT!Inti De Ceukelaire made $50K in just a few weekends. Without using any proxy interceptors or scanners. He took to the stage at DefCon 2026 to discuss everything he did to achieve this. Here’s a sneak peek regarding his findings on crawlers! “What do most of these crawlers do? They look for a set of common things like sitemaps. Whenever you give it a domain, it's always going to look at the sitemap. But there's quite an interesting namespace attack that you can then use. I've been calling myself
- AI can help security teams and researchers find more potential issues faster. But more findings do not automatically mean more security. When finding bugs gets cheaper, the challenge shifts: which issues are real, exploitable, and worth fixing? In our latest blog, Chris Holt explores the difference between paying for testing effort and paying for validated impact, and why human context, triage, and remediation matter in an AI-accelerated world. “The hype that worries me is that some vendors position AI as if it is an autonomous
- When PHP2Shell was disclosed, the data told a story. 🧐 Across active programs, our global researcher community provided a unique view into how the vulnerability unfolded in real time, revealing patterns in researcher activity, organizational response, and security exposure. We’ve brought those observations together in a new insights report, exploring what the data reveals, how PHP2Shell compares to previous critical vulnerabilities, and what the findings can teach us about responding to the next one. Explore the data. Read the
- If you’re a security professional in the UK, this one’s for you. 🇬🇧 Hackers in the House is back in London on December 11, 2026, putting security researchers in the room with the civil servants shaping UK cyber policy. Topics on the table include the forthcoming Cyber Security and Resilience Bill, secure-by-design practices in AI, vulnerability research, and more. No policy experience needed, the event kicks off with sessions to get you up to speed before you head into your government briefings. And it’s completely free to attend.
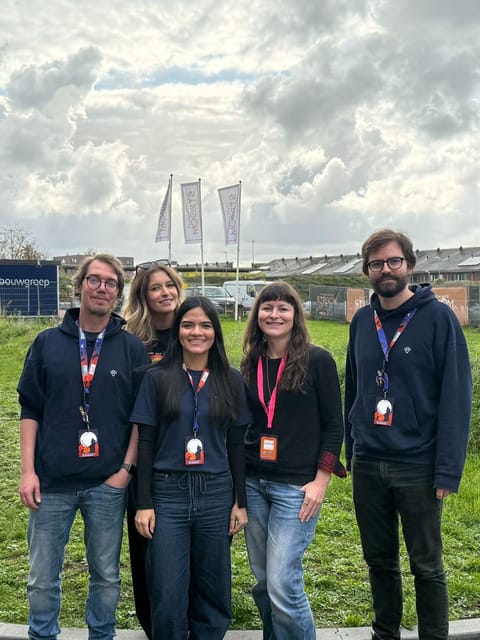
- WICCON is a wrap! 💜 Two days in Haarlem with some of the most passionate people in the cybersecurity space. It was brilliant to be part of an event built around empowering women in security, and even better to meet so many of you in person. 🌟 Thank you to the WICCON team for putting together such a welcoming event, and to everyone who stopped by to say hi. See you at the next one! 🤠 #WICCON #WomenInCybersecurity
- Asking your AI agent to summarize a web page shouldn’t leak your one-time password. With indirect prompt injection, it can. 😈 Hidden instructions in content an AI agent reads, like an email, a web page, or even a Reddit comment, can trick it into leaking sensitive data using access it already has. Brave’s research on Perplexity Comet showed exactly that. Swipe to learn more about indirect LLM prompt injections. 🎃 Have you found prompt injections in AI features before? Share your story in the comments! 👇 #bugbounty
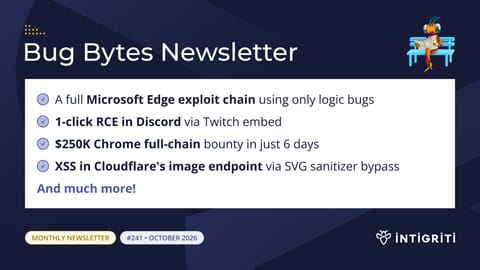
- Latest Bug Bytes is live! 🚀 This month's issue is as usual packed with bug bounty tips: ✅ A full Microsoft Edge exploit chain using only logic bugs ✅ 1-click RCE in Discord via Twitch embed ✅ $250K Chrome full-chain bounty in just 6 days ✅ XSS in Cloudflare's image endpoint via SVG sanitizer bypass + company updates & much more! 😎 Read the latest issue now! 👇

Alumni 1 went on to found or lead
 Inti De CeukelaireChief Hacker Officer→Integrated AI Security Researcher & Founder at INTI
Related profiles
Something wrong or missing? Send an update. Fixed within 24 hours.