
Overview
Refracted Security provides cybersecurity consulting services including pentesting, red teaming, ethical hacking, vulnerability assessments, threat hunting, incident response, and security training. The company helps organizations check their security posture and offers VLAIO-funded cybersecurity improvement programs for Flemish SMEs and NIS2 organizations.
Key people
In the news
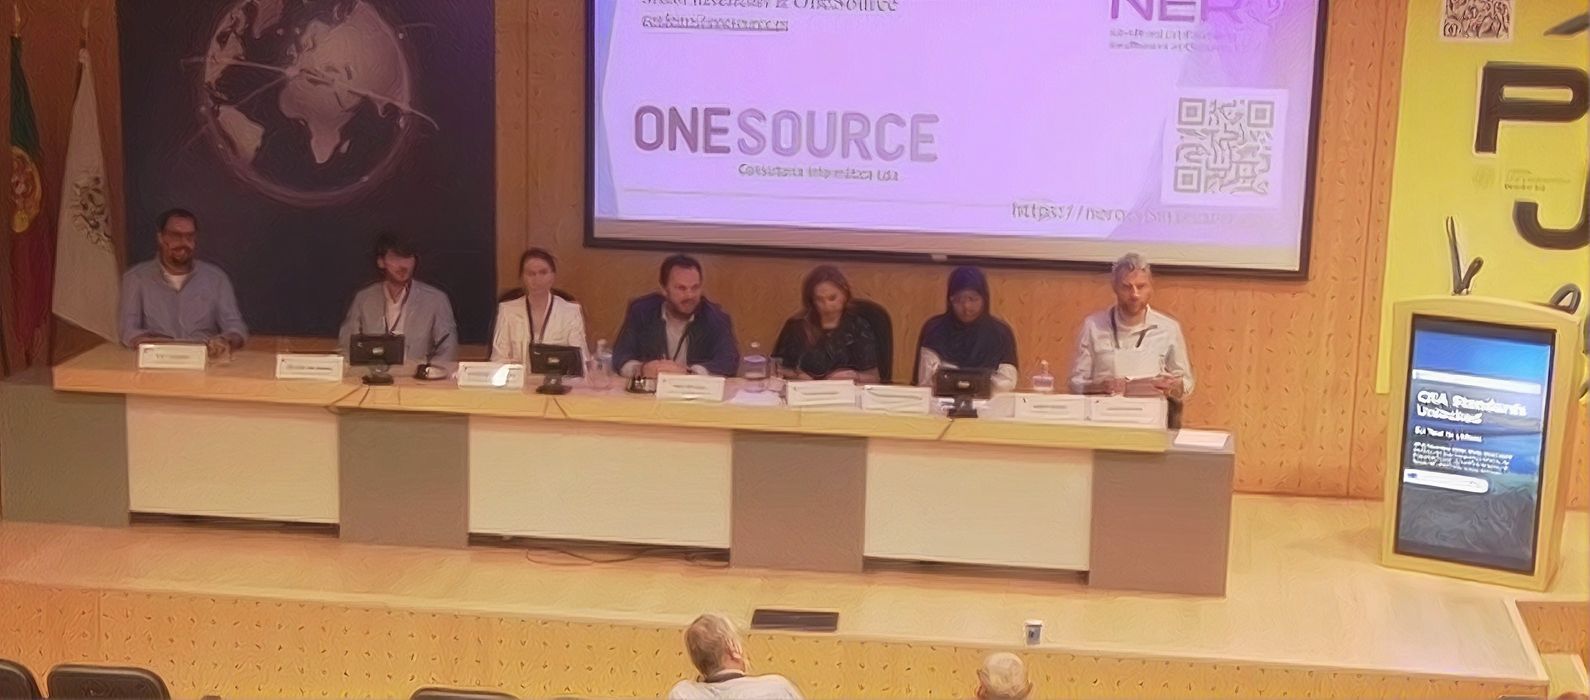
- A day packed with Cyber Resilience Act (CRA) activity across Europe! It has been a busy day for Refracted on the CRA front with activity spanning multiple European initiatives and communities. Our esteemed CEO Ben Van Erck was present at the CRA Unlock Tour in Lisbon, connecting with stakeholders and exchanging perspectives on the implementation of the Cyber Resilience Act. Meanwhile, our colleague Siebe De Roovere joined our partners at CRANIUM and Cingulum for a dedicated webinar on the CRA, bringing together several essential
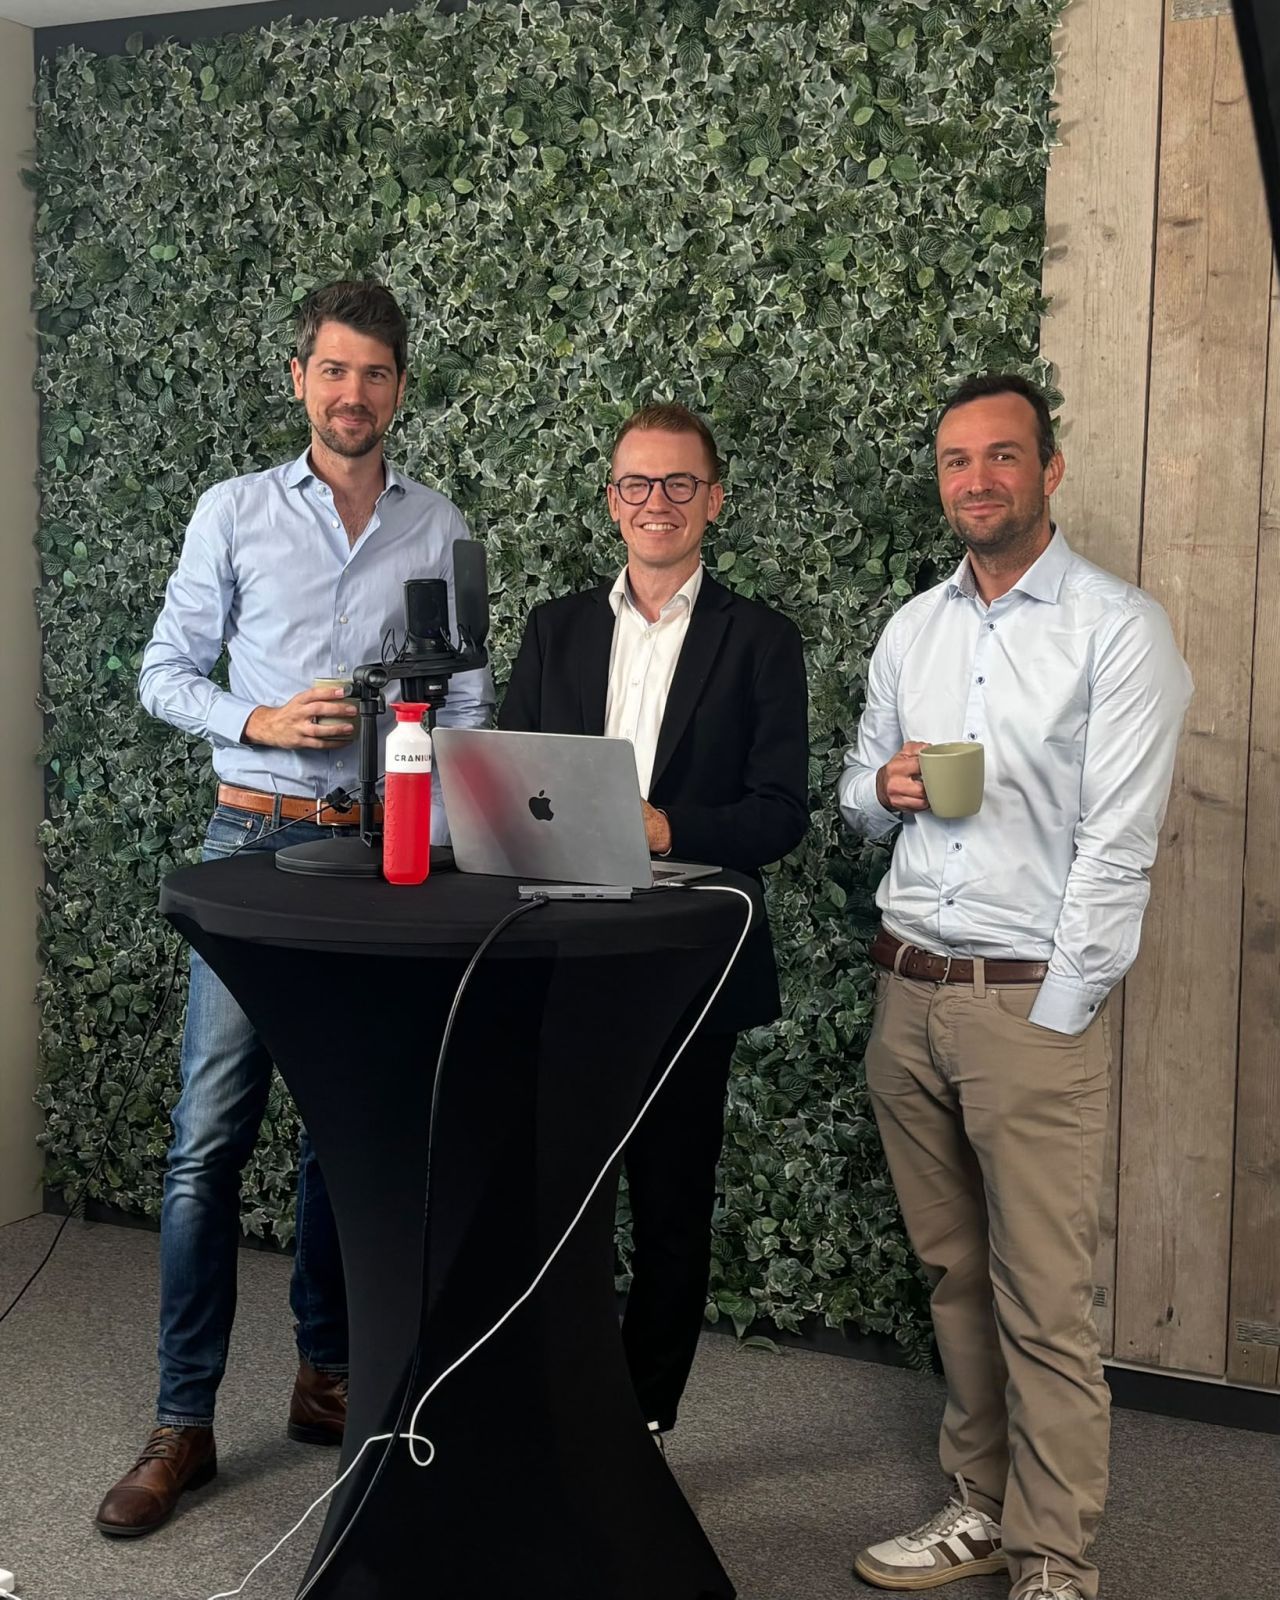
- Last call 🚨 Schrijf je nog snel in! Tijd om mee te zijn met de Cyber Resilience Act. Morgen leggen we het uit, samen met Cingulum en Refracted Security. Zit je met vragen over de CRA? Je kan ze morgen stellen. 👩💻 17 september, 13u-14u 🔗 https://loom.ly/3fse4sI Kan je niet live volgen? Schrijf je toch in en ontvang achteraf de opname en de slides.
- Beste vrienden, 🚀 De laatste rechte lijn richting ANNACON 0x7EA is ingezet. Hoog tijd dus om 21 oktober 2026 in je agenda te blokkeren en je in te schrijven, mocht je dat nog niet gedaan hebben. 📍 Provinciehuis Antwerpen Voor wie ANNACON nog niet kent, zetten we graag nog eens op een rij wat je mag verwachten: 📢 Een volledige dag cybersecurity talks én netwerken ‼️ Volledig gratis ✨ Gegarandeerd niet-commerciële talks 🎉 Twee parallelle tracks 👔 Een beleidstrack voor de suits 🥷 Een technische track voor de hoodies ⛳ Een
- Every product company will eventually get that email: "I found something in your product." What happens next is not a technical question. It's an organisational one. Who receives it, who decides how bad it is, who talks to the customer, and who signs off on the timeline. The CRA turns that from good practice into a legal obligation: vulnerability handling, SBOM, coordinated disclosure, and notification to ENISA within 24 and 72 hours. Core requirements apply from December 2027. We build that capability with product teams from an
- Hoe cyberveilig is de Belgische 𝗯𝗼𝘂𝘄𝘀𝗲𝗰𝘁𝗼𝗿? Over exact één week deelt onze CEO Ben Van Erck de resultaten van onze recente cybersecurity scan in de Belgische bouwsector tijdens het Greyn Market launch event! 💡 Blijf niet achter op het vlak van digitale veiligheid en ontdek hoe je jouw organisatie beter beschermt. Hopelijk tot dan! #CyberSecurity #Bouwsector #GreynMarket
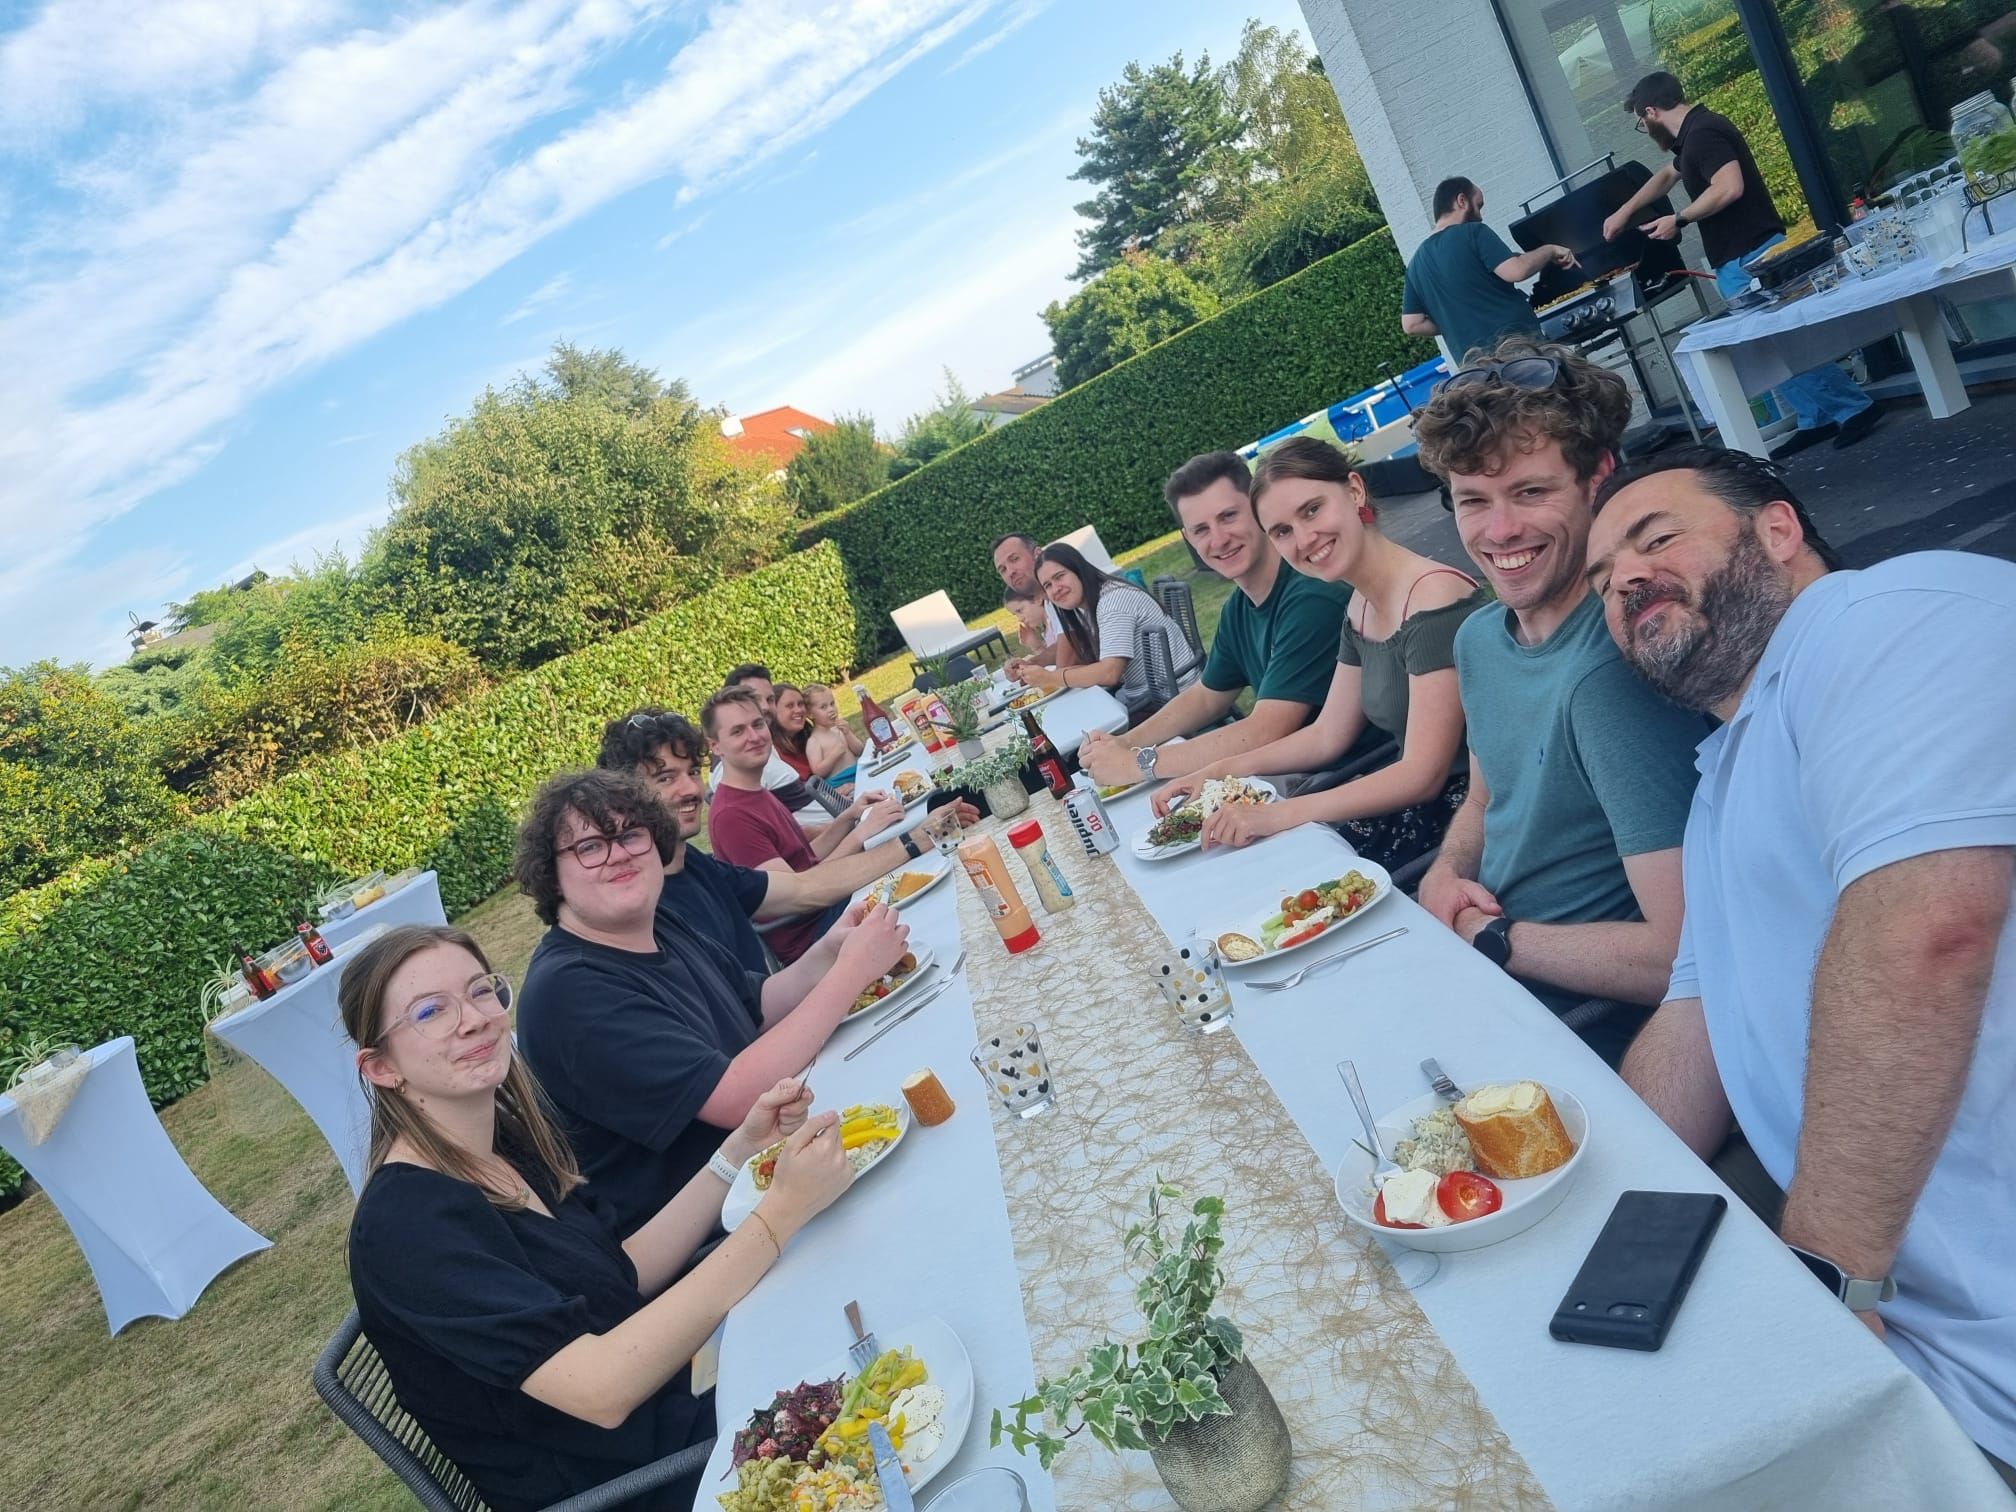
- Closing off summer with a BBQ surrounded by colleagues, friends and family. Re-charged for a busy last quarter, and let's be honest with the current weather, sitting behind our computer isn't that bad 👩💻.
- As of 11 September, the reporting obligations under the Cyber Resilience Act apply. By the end of 2027, your organisation needs to be fully in order. Together with CRANIUM and Cingulum, we'll walk you through the key changes in one hour: what falls in scope, how to set up vulnerability management, SBOM handling and coordinated disclosure for the 24 and 72 hour reporting window, and which demonstrable artefacts supervisors actually expect. Complex regulation, brought back to what it practically means for your products. Free webinar on
- Verkoop je digitale producten en hoor je het donderen in Keulen bij CRA? Dan is onze volgende webinar wellicht voor jou! Vanaf 11 september gaat de Cyber Resilience Act in voegen en moet ook jij eraan voldoen als je digitale producten verkoopt binnen de EU. Wil je graag bijleren over de impact op juridisch, technisch en governance-vlak? Onze expert Bernd Fiten , en collega's Stijn Muylle (Cingulum) & Siebe De Roovere (Refracted Security) nemen je mee in het volledige verhaal. 👉🏽 Schrijf je nu in voor onze webinar op 17 september om

Something wrong or missing? Send an update. Fixed within 24 hours.