Overview
Damian Myles is a co-founder of Crimson7, a role he has held since January 2025, and is based in Maastricht. He co-founded Route443 in November 2020 and remained until October 2025, having earlier been managing partner of ROUTE443 LLP from 2016 to 2020. In June 2012 he co-founded PointSharp Benelux BV, a role he held until July 2023.
His earlier career combined consulting and architecture work. He was a security consultant at PwC Belgium from 2019 to 2020, and had held the same role at PwC in 2015. Between 2015 and 2018 he was identity and access architect at Darling Ingredients Inc., and he was cloud security architect at the Belgian Post Group from 2012 to 2014. He worked as an infrastructure architect at OCI Nitrogen, Essent, DSM and Capgemini, and held further consulting and engineering roles at Van Gansewinkel, Sitech Services BV, Hewlett Packard Enterprise, Mobile Communications AS, Vendinova IT Solutions and Sopheon NV.
He studied business management at the University of Brighton, graduating in 1992.
Career history

In the news
- We've shipped an MCP server for the Crimson7 platform. Anything you can do in HackerFlow and 7Hunter, an agent can now do through it. The server exposes the two products' operations as tools an agent can call: browse the scenario library, launch an execution, read the detection result back, pull the coverage report, write and run a hunt query. Point that same agent at your threat intel feed (like our partner Tidal Cyber) and it can work out which groups actually go after an organisation of your sector and your size, then execute
- Today, we welcome Liam Deferm to the Crimson7 family! Liam is an offensive security specialist, experienced in DORA TLPT and TIBER-BE red team operations in high-complexity environments. He also specialises in malware and command-and-control development, building the custom tooling that keeps our engagements realistic rather than off-the-shelf. Beyond client engagements, Liam will feed directly into our product development, expanding the attack scenarios and techniques we test against, so our clients are measured against what
- There is no patch for CVE-2026-50656, but there is a detection rule in 7Hunter. Microsoft's own advisory reads E:F/RL:U: functional exploit code exists, no remediation available. The ShieldBreak PoC dropped Tuesday, and it takes a standard user to SYSTEM on Windows 11 25H2 and Server 2025 with a claimed 100% success rate. What makes ShieldBreak worth reading is not the escalation, it is the write primitive. There is no vulnerable driver in this chain. The exploit registers a rogue cloud sync root, chains Object Manager symlinks, then
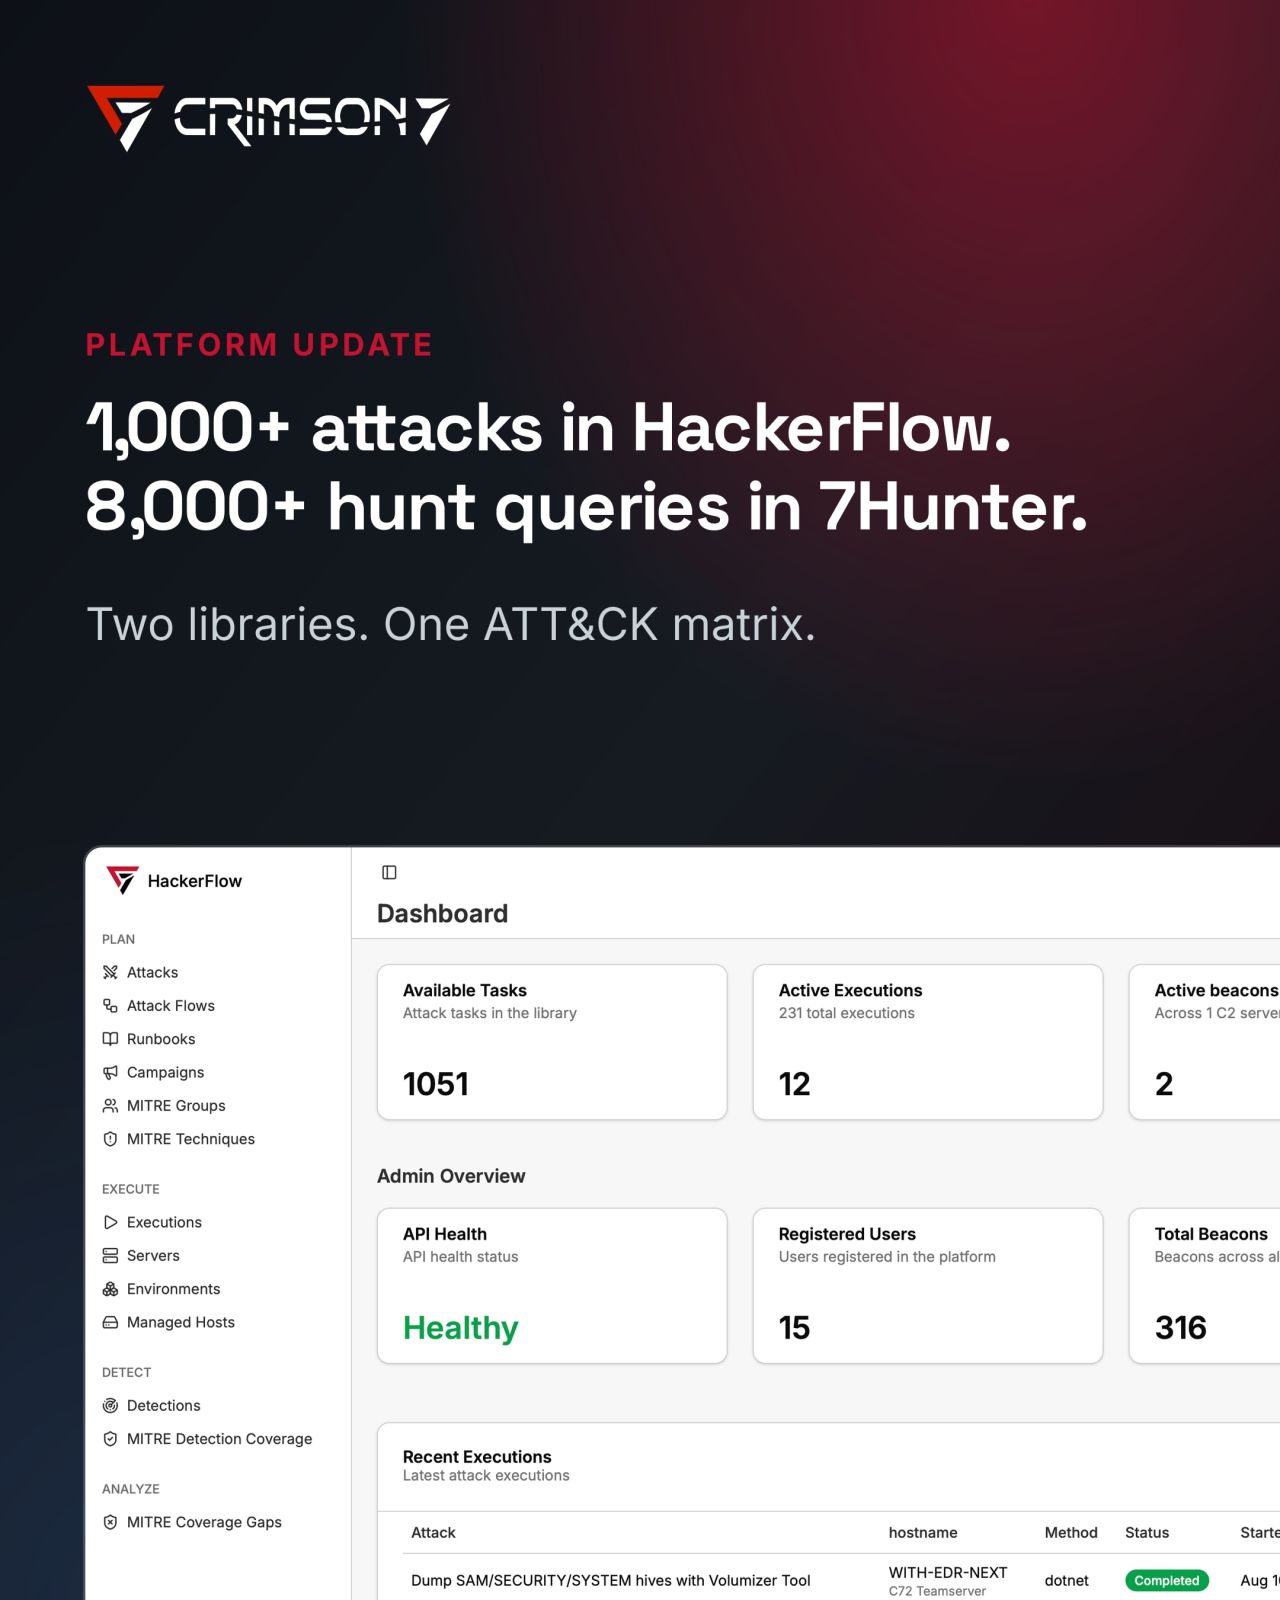
- We've shipped a major update to the Crimson7 platform. HackerFlow now carries 1,000+ attack scenarios, 7Hunter 8,000+ hunt queries. Run an attack technique, watch nothing happen in your security tools, and you can go straight from the absent detection to deploy ours and perform the hunt query covering that same technique, to check whether it already happened in your environment. Attack coverage and hunt coverage now go fully hand in hand. Both products now carry a chat assistant with full context on the workspace around it: your
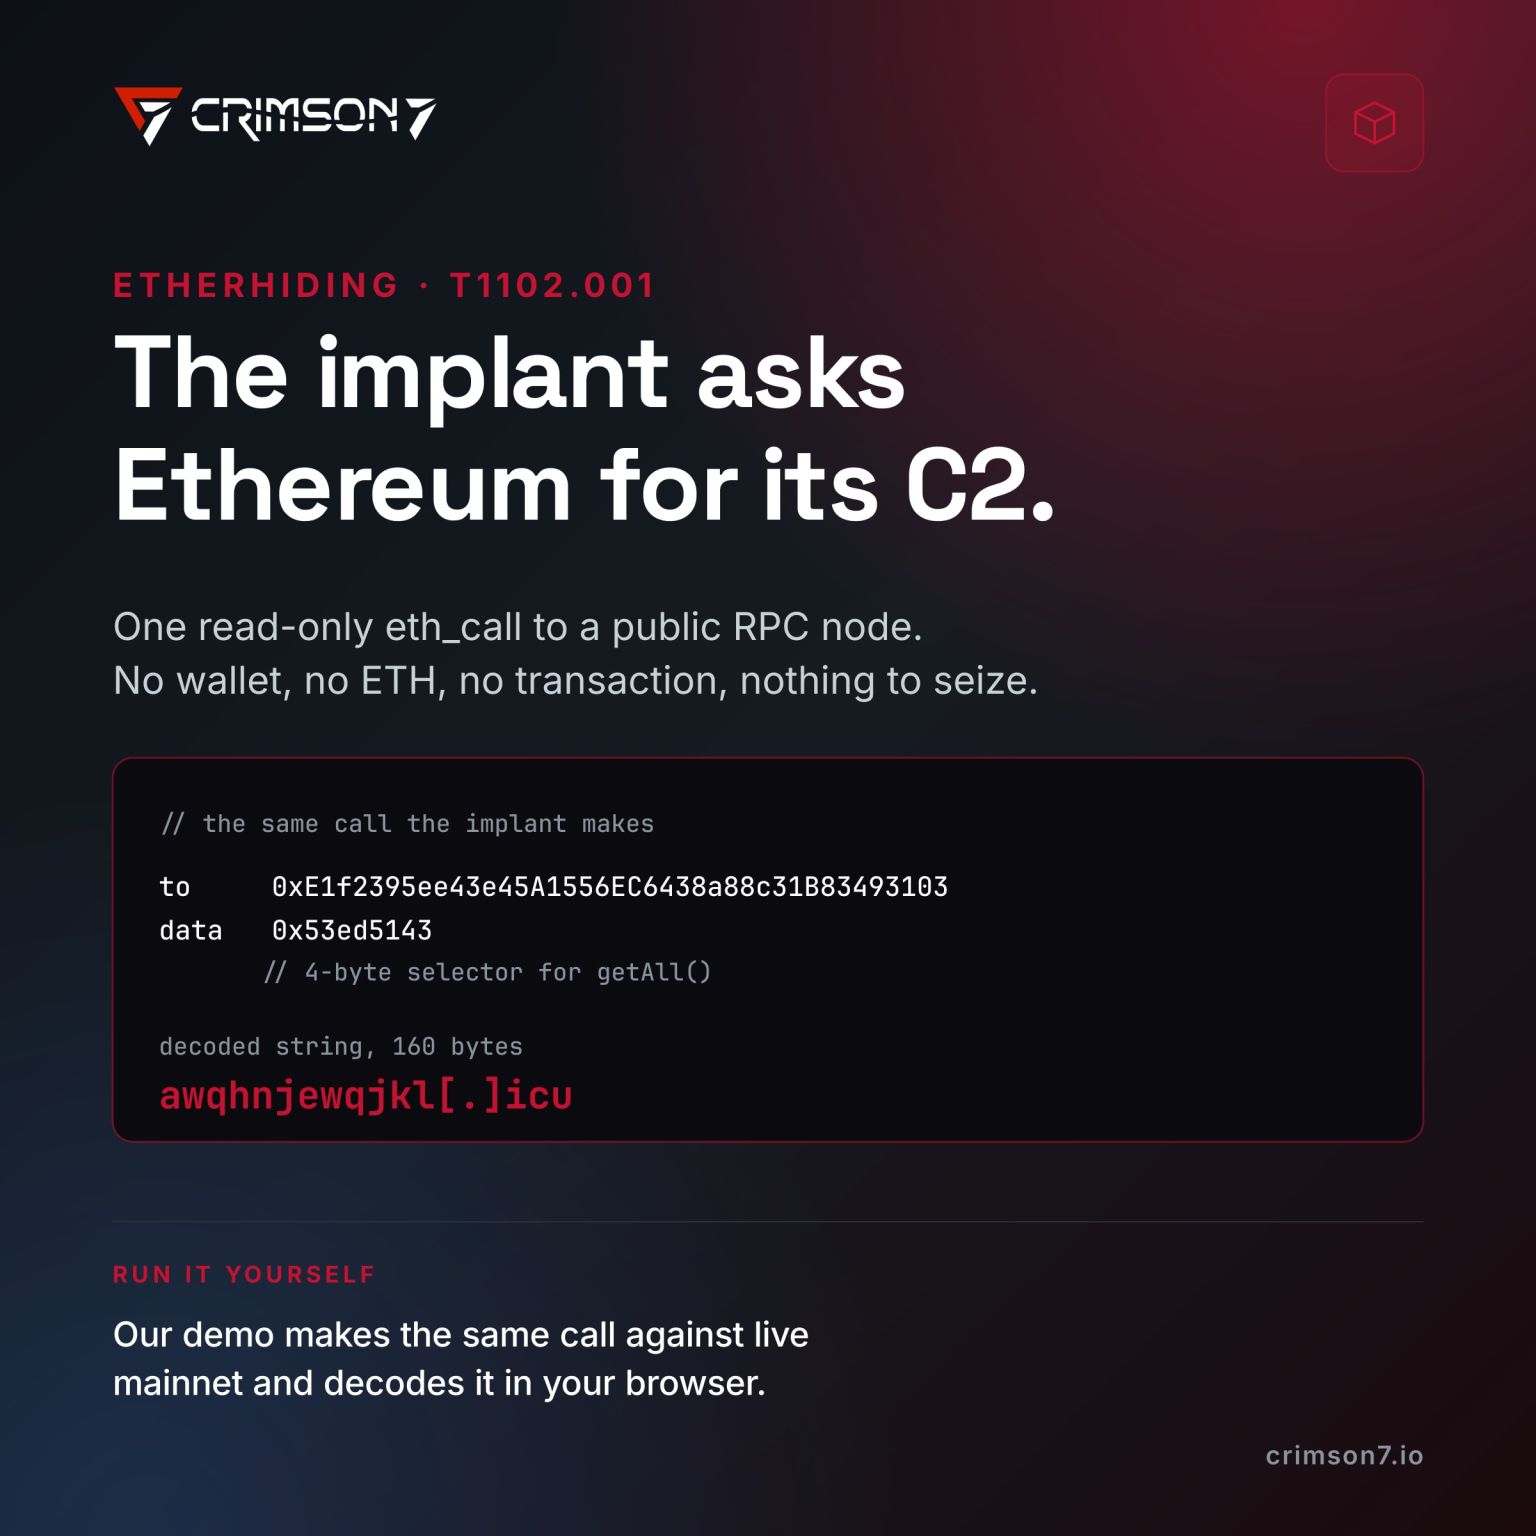
- The malware does not carry a C2 domain. It carries a contract address and asks Ethereum for the domain at runtime. That is EtherHiding, MITRE T1102.001, and it is active in the Shai-Hulud npm campaign. The read is free and silent. No wallet, no ETH, no signature, no transaction. The implant sends one eth_call to a public RPC endpoint with a 4-byte function selector and gets a string back. Nothing lands on chain, so there is nothing to trace back to an account. Which leaves defenders with no takedown path at all. No registrar to
- Jeff Schiemann has spent more than two decades as the buyer we build for: a security leader carrying real risk, most recently as CISO of a regulated Swiss bank specializing in Securing Digital Assets and Web 3 Security. He joins Crimson7 as Advisory Board Member and Customer Evangelist. "We break defenses for a living. The quiet risk in that work is drift: you start optimizing for attacks that are elegant instead of the ones that keep security leaders awake. The correction is to put a practitioner in the room and give them a real
- Yesterday we posted a summary of the Shai-Hulud npm compromise done by our research team and enriched by Aikido Security's write-up. Credit to them for the early analysis of the affected packages. It is where most of us started. Since then we took the sample apart ourselves. keyv@6.0.0 ships no hardcoded C2 domains. It carries an Ethereum contract address and asks the blockchain for its current exfiltration endpoint at runtime. Domains rotate for the price of a transaction. The contract address does not, because changing that means
- Today we welcome Michele Negri to the Crimson7 family. Michele is a cybersecurity professional with professional experience in red teaming and blue teaming with a strong focus on Windows environments and Active Directory security both in offensive and defensive way. He has worked on offensive security engagements and incident response on complex internationals enterprise infrastructures. He also has deep interest in low-level study and research, operational security and cloud security
Related profiles
This page shows public professional information only, each fact cited. Is this you? send a correction, or ask for removal within 24 hours, no questions asked.