
Key people
In the news
- Loved being part of the Fundtruck stop in Brussels! Our co-founder Babette De Decker took the stage alongside 15 fantastic startups from across Belgium. It was a great opportunity to pitch Nemesis to a jury of ecosystem experts at Greenbizz.brussels and share how we’re building continuous security validation. Huge thanks to the organizers, jury, and fellow founders for such an inspiring day 😃 🎥 Video Credit: Maddyness #Nemesis #securitycontrolvalidation #ThreatToTest
- Meeting DORA requirements like Articles 25 and 26 means moving beyond basic self-assessments and actively testing how your defenses hold up against real threats. Here is a look at how Nemesis maps threat emulation directly to these mandates to give you repeatable, auditable proof. Link: https://lnkd.in/dB2KTNWD #DORA #securityassessment #Nemesis
- Great to see our team featured in the latest spotlight from the Belgian Cyber Security Coalition! Our co-founder Babette De Decker spoke about how she went from international relations to building Nemesis, why cybersecurity needs diverse backgrounds, and how we’re making security validation more accessible for teams everywhere. Link: https://lnkd.in/eQ_gAKrd #Nemesis #ThreatToTest #cybersecurity
- Nikos Laleas from our team took the stage at the Net++ technology event to show how Nemesis runs live, continuous attacks to see what security controls actually hold up. A huge thanks to the Net++ team for putting together a great session at Hard Rock Cafe, it was awesome catching up with everyone and talk cybersecurity in such a fun setting. #Nemesis #securitycontrolvalidation #ThreatToTest
- A big shoutout to the team at Calif for the discovery of PHP2Shell (CVE-2026-109618 & CVE-2026-109619). Publishing a patch is only half the battle, you still need to confirm it actually works and keep your WAF rules and detections tightly under control. That's why our team built and validated automated attack simulations in Nemesis within 24 hours of disclosure. That’s why Nemesis runs real attack techniques safely against your systems, proving whether your defenses actually stop threats instead of just hoping they do. Link:
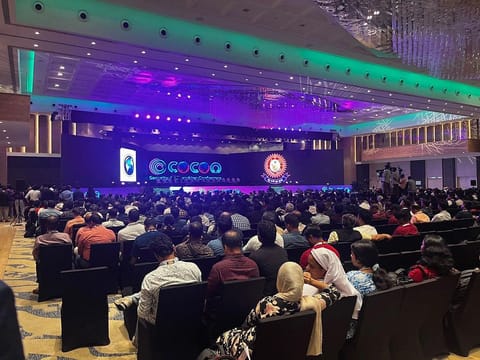
- Conversations at c0c0n 2026 made it clear that enterprise teams want advanced security validation, but they aren’t willing to compromise on data privacy or send sensitive logs to external clouds. That exact challenge is why we built Nemesis to run locally on-premise with zero data leakage. It was great discussing these security hurdles with fellow defenders at the conference. Blog Link: https://lnkd.in/ezzAbq99 #ThreatToTest #securitycontrolvalidation #Nemesis
- Some environments thrive in the cloud, while others demand strict on-premise control, especially in regulated sectors. Nemesis handles both effortlessly by running a local AI model right inside your own system. It’s built to give you continuous attack validation without forcing you to compromise on where your data lives. #LocalAI #ThreatToTest #Europe #securitycontrolvalidation
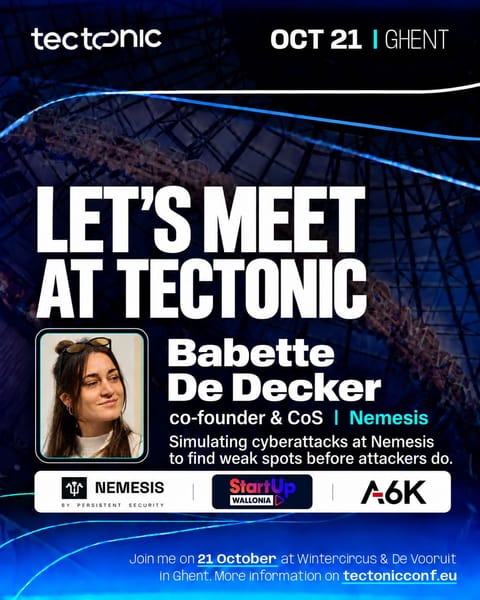
- We’re heading to Tectonic and our co-founder Babette De Decker will be on the ground representing the Nemesis team. She’s really looking forward to catching up with familiar faces, making new connections, and having honest conversations about where security defenses usually break down. It’s always great getting to connect with the community in person, so if you’re attending, feel free to say hi! 👋 #Techtonics2026 #Networking #cybersecurity

Alumni
 Markus VervierChairman→Managing Director at X41 D-Sec GmbH
Something wrong or missing? Send an update. Fixed within 24 hours.