Overview
Markus Vervier is chief executive officer of persistent-security and is based in Aachen. He has been a director of Persistent Security since August 2022, and served as its chairman from August 2022 to March 2025. Since December 2016 he has also been managing director of X41 D-Sec GmbH, and from January 2019 to November 2023 he was managing director of mstorm.io.
Earlier in his career he was a senior security consultant and software developer at LSE Leading Security Experts GmbH from October 2011 to December 2015. He worked as a professional services engineer at Atronos Solutions GmbH from May 2008 to September 2011, and was a diploma student at CanControls between June 2010 and February 2011. From March 2005 to August 2007 he handled IT coordination and software development at Kulturserver gGmbH, and from October 2004 to May 2007 he worked in IT security as a penetration tester at RedTeam Pentesting GmbH.
He holds a Diplom in Informatik from RWTH Aachen University. His stated areas of expertise are cybersecurity, penetration testing, red teaming, reverse engineering and source code auditing.
Career history

In the news
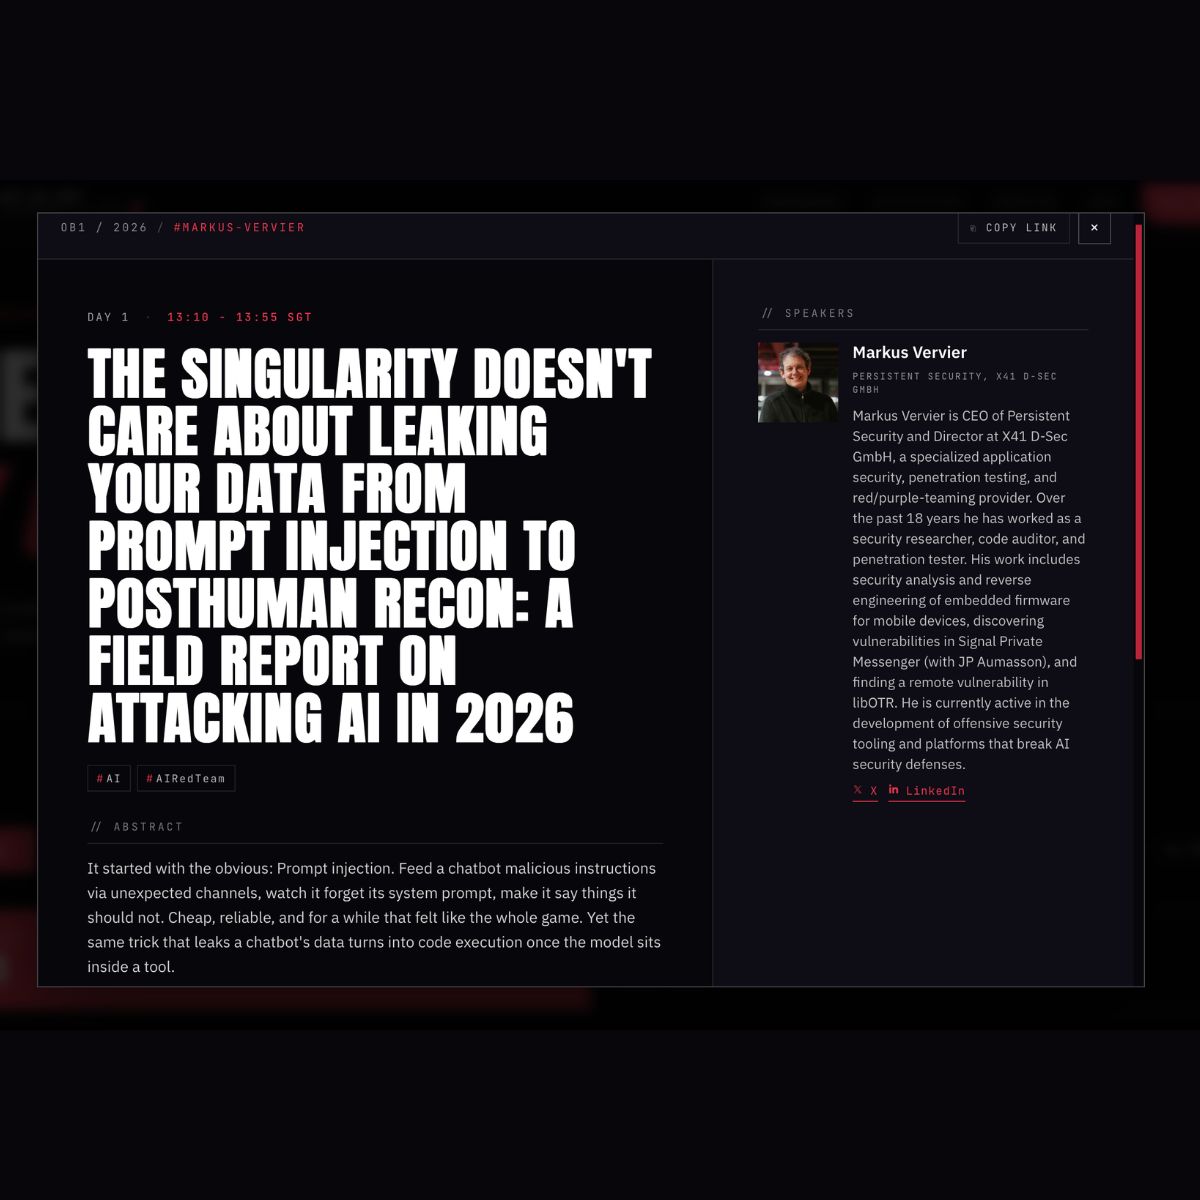
- Thank you Off-By-One Conference for having me speak about my research about what AI means to the security space. We will go from applying AI to attacking AI itself and the implications this has on the security auditing, pentesting and last but not least novel types of security automation platforms. Plus we will get a glimpse of my upcoming Phrack paper featuring how AI models themselves can be infected by a novel kind of malware and create their own class of security issues. (More info in the comments below)
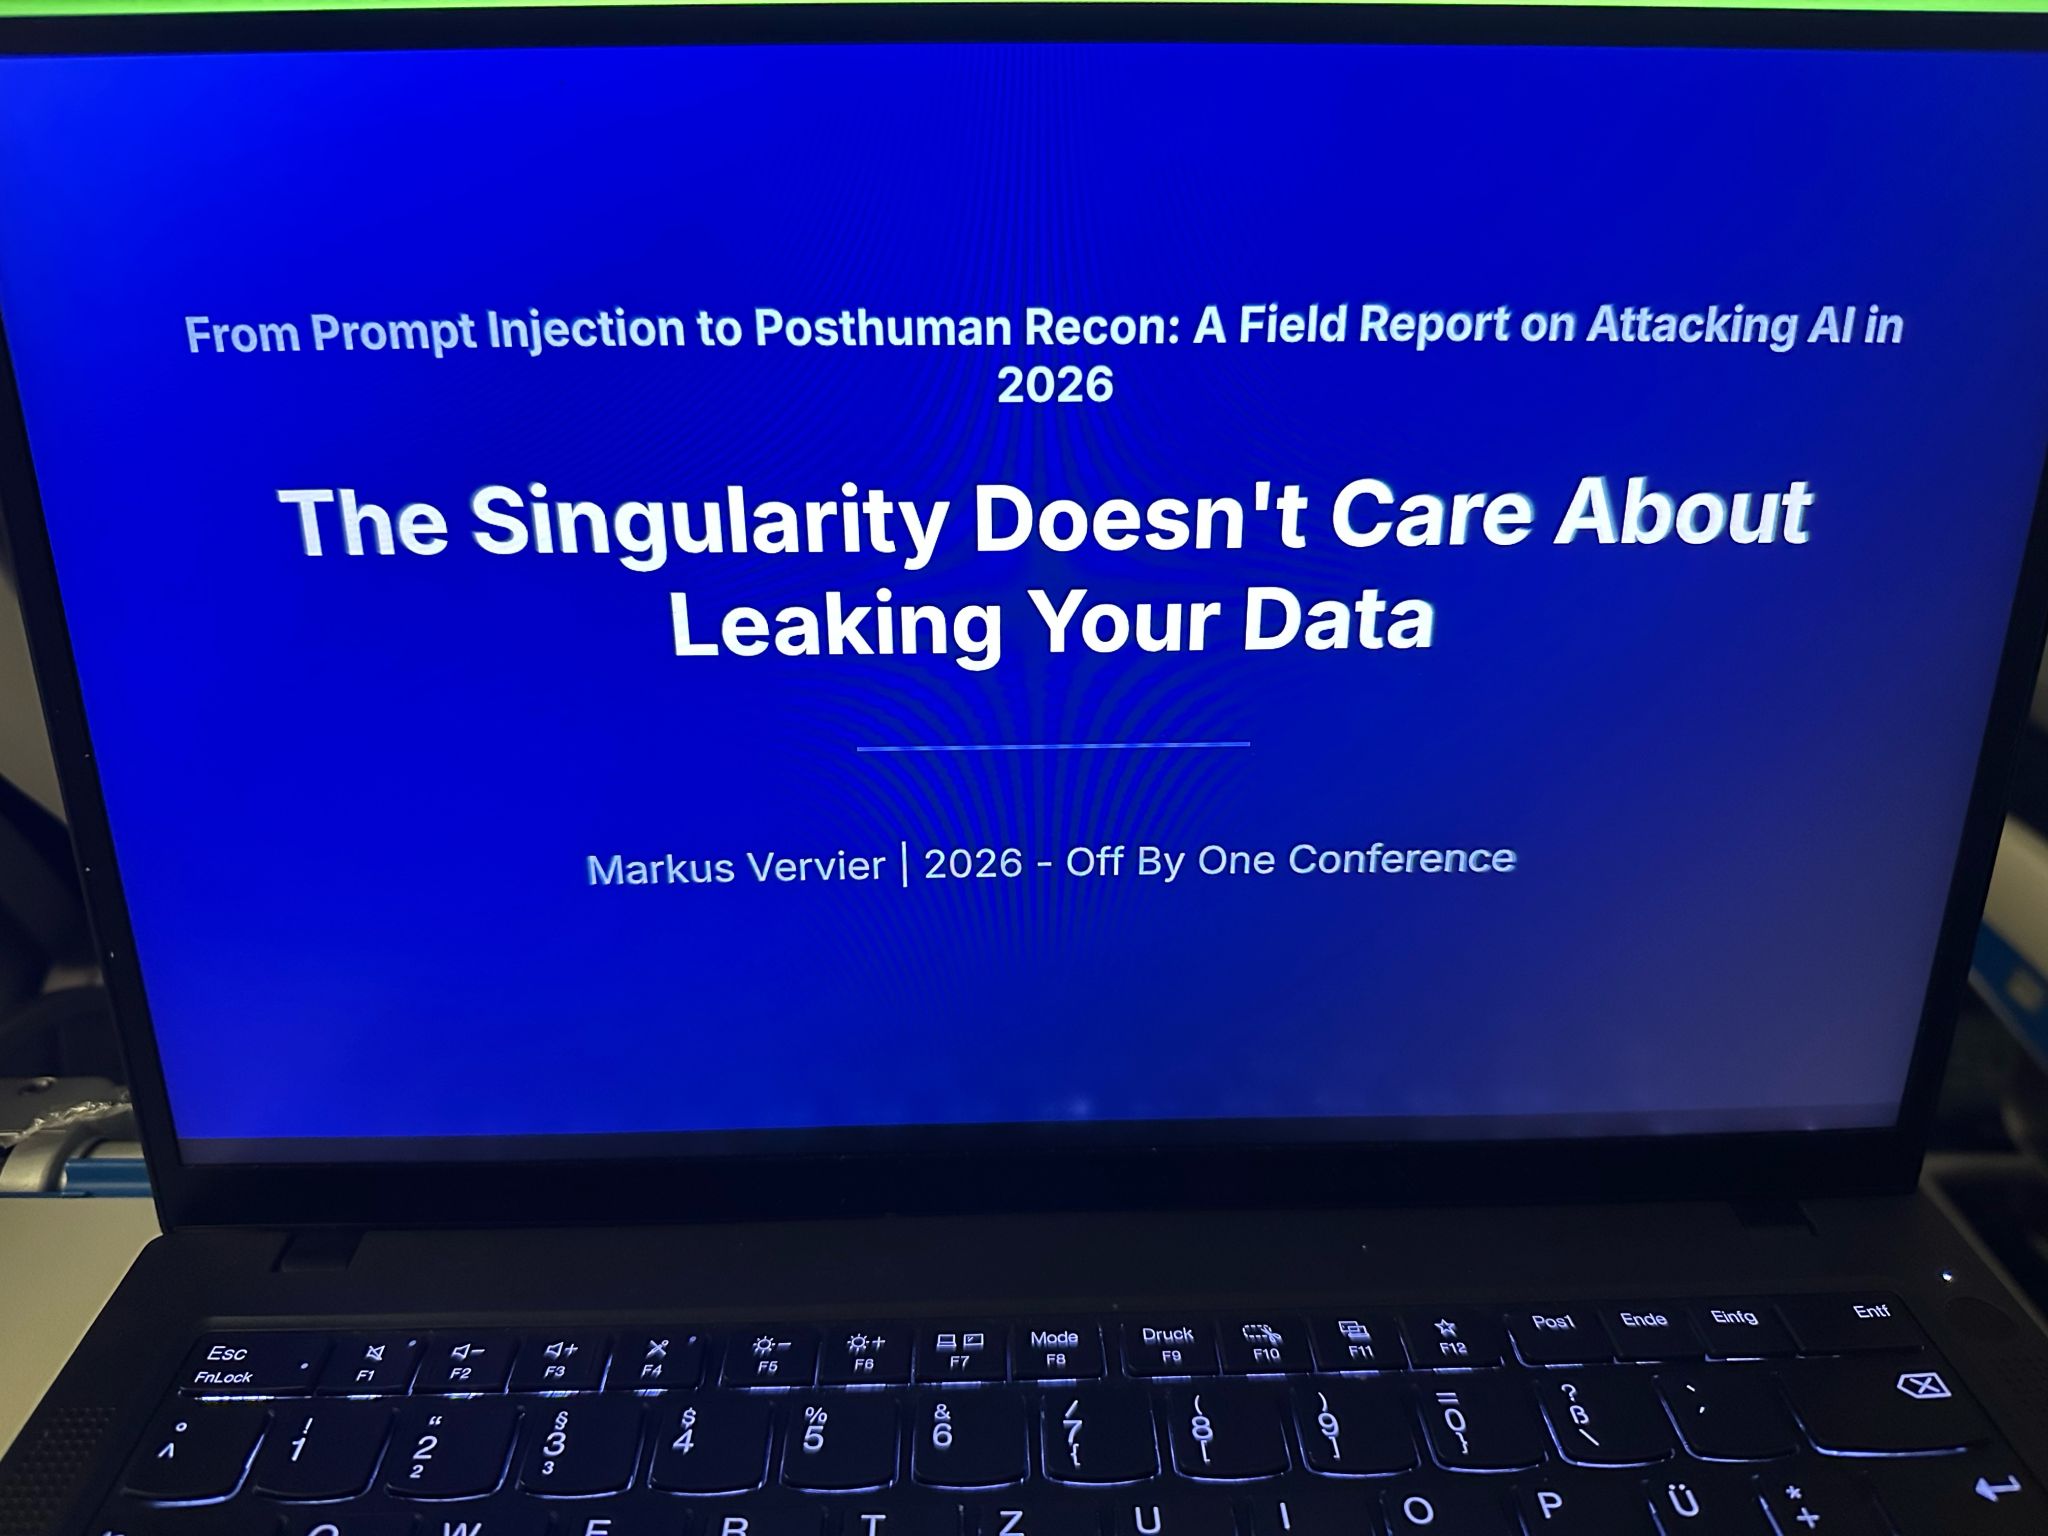
- Markus Vervier is taking the stage at Off-By-One Conference in Singapore to break down the sheer chaos of AI security in 2026! Between indirect prompt injection and models executing untrusted code, context has officially become the new attack surface. If you’re at the event and want to catch up with the Nemesis team, feel free to drop us a line! Talk Details: https://lnkd.in/dxZeHKHN #OB12026 #OffByOne2026 #offensivesecurity #AIForSecurity
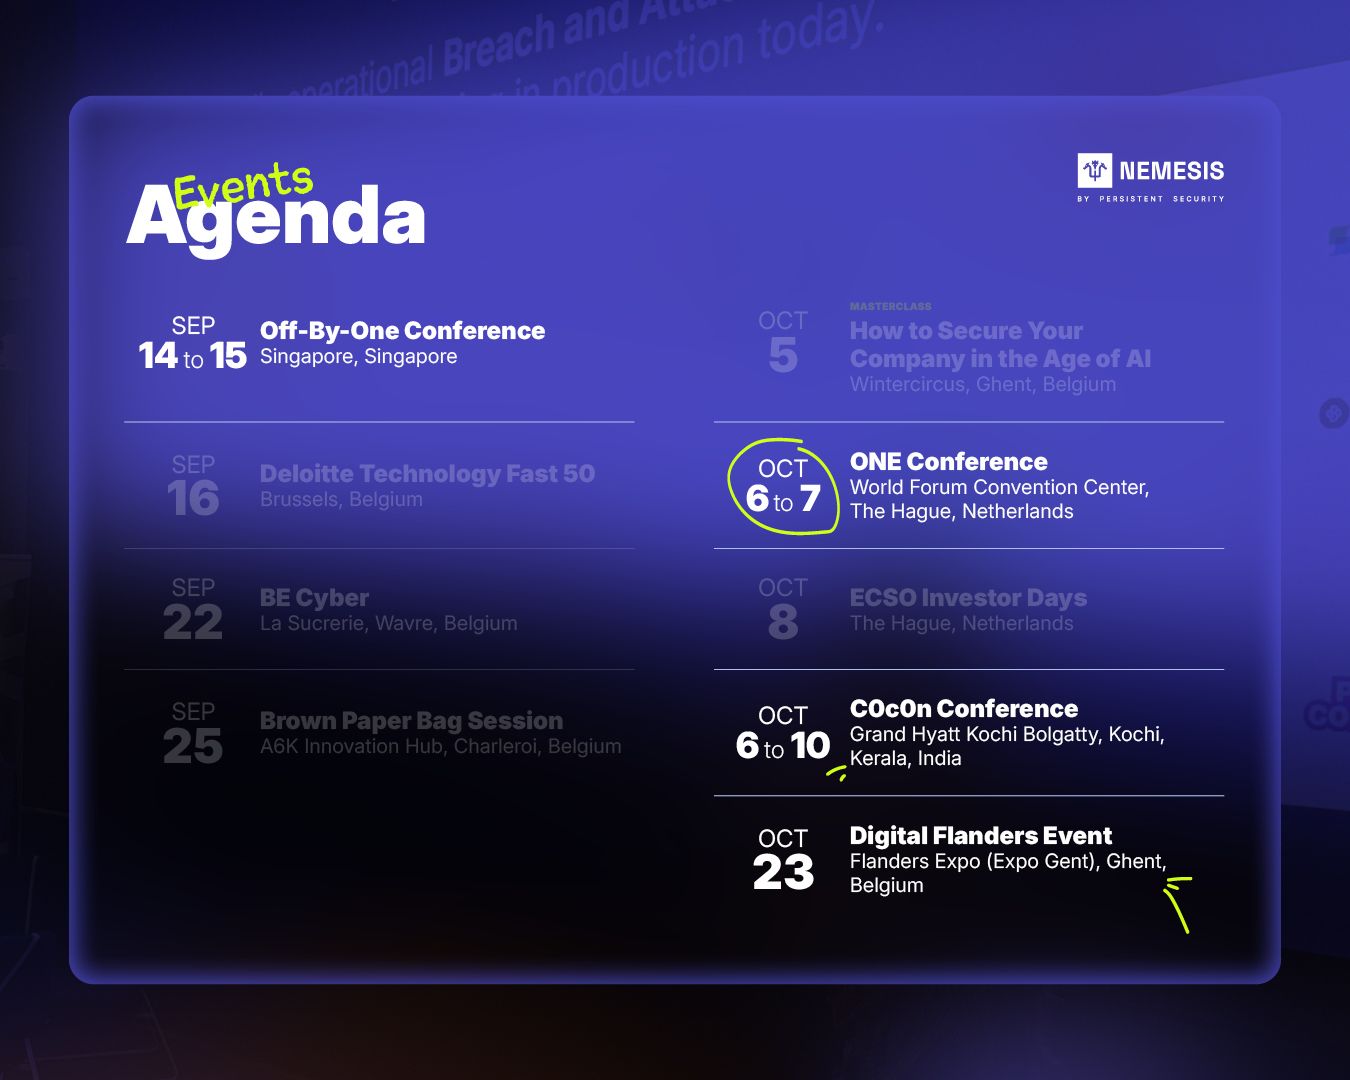
- Markus Vervier’s event schedule for September and October is officially locked in! As CEO and Technical Co-Founder at Nemesis, he’s excited to connect with SOC leaders, MSSPs, and privacy first innovators across the globe. At Nemesis, we’re revolutionising security control validation with our independent, on-prem local AI that replaces static scripts with dynamic, continuous threat testing. Take a look at the schedule below and send over a message if you want to connect. #ThreatToTest #SecurityValidation #AIForSecurity
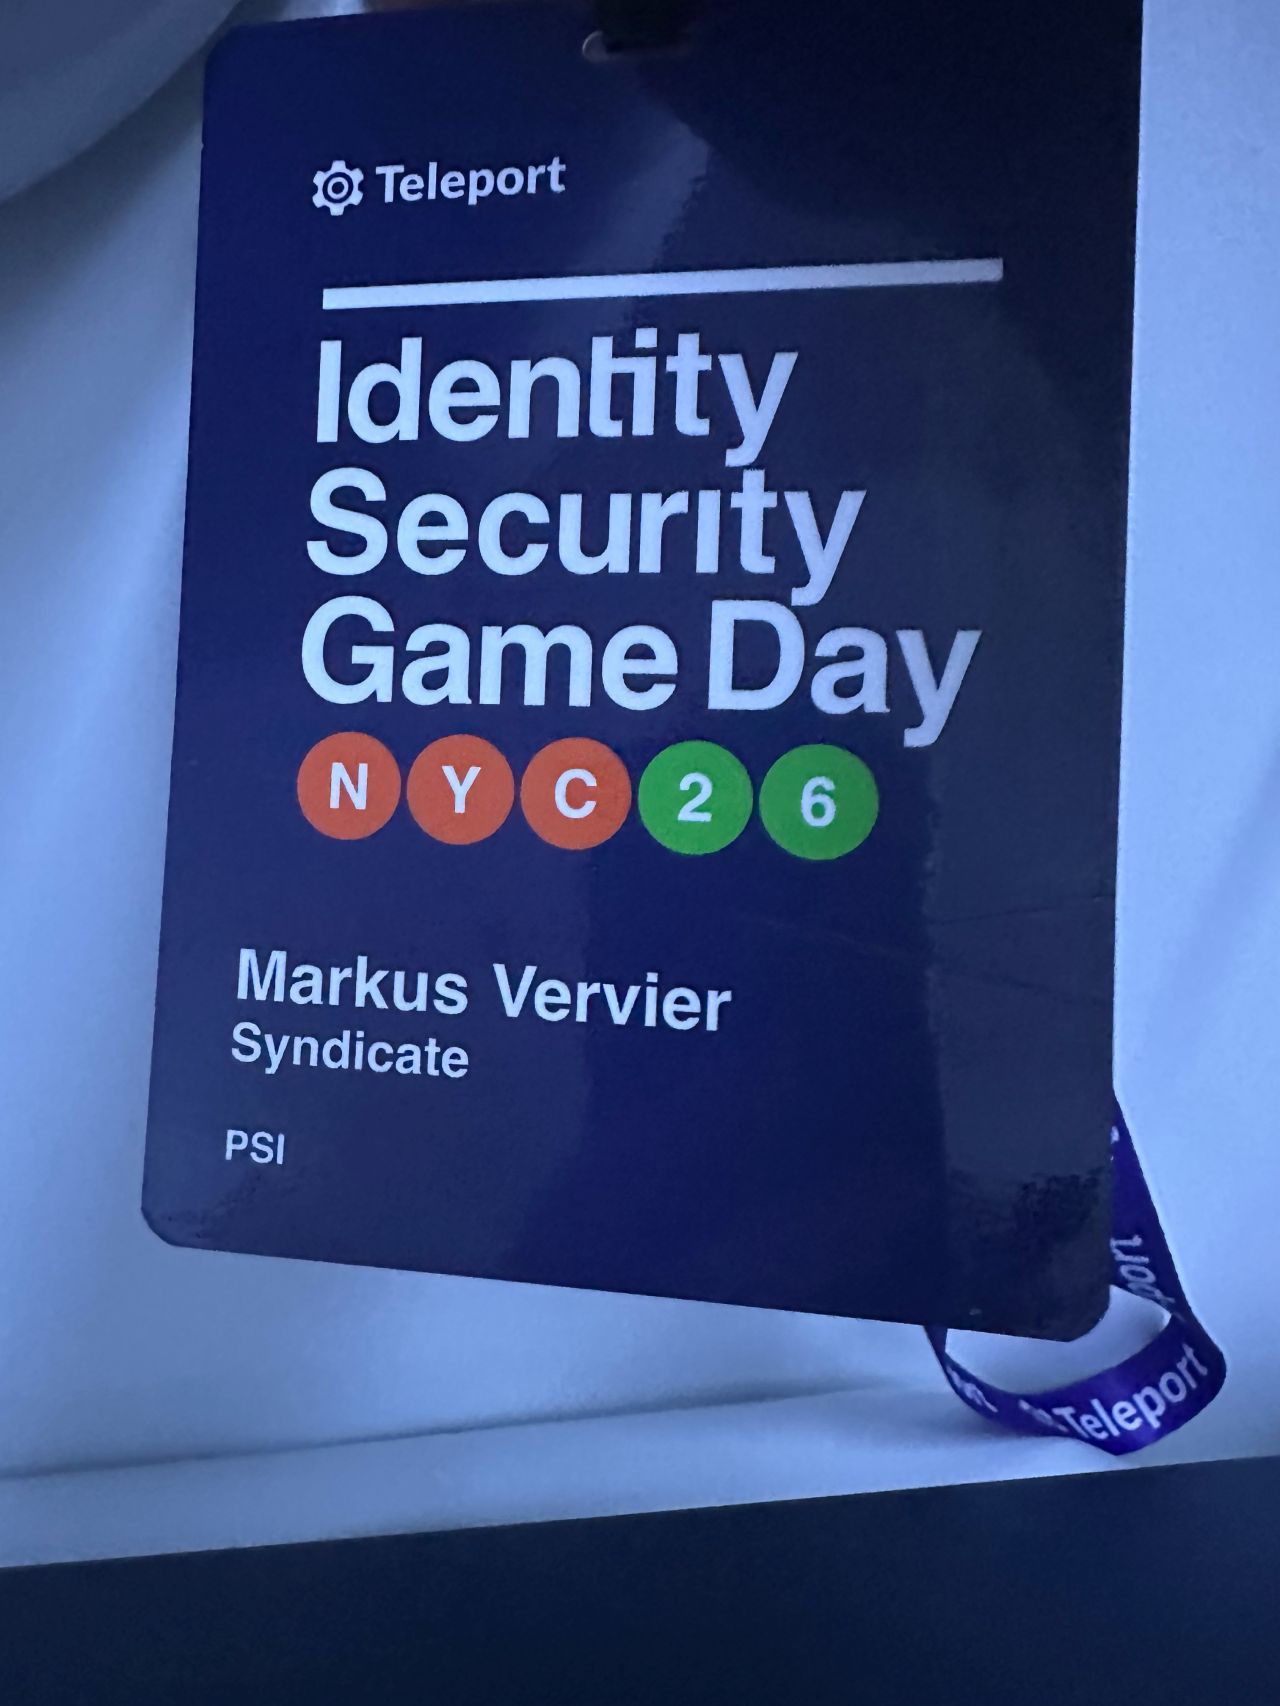
- Bye NYC, had a blast at the security Gameday and on the panel of the Speakeasy with Ben A. and Rob Picard, applying and discussing AI in offensive security!
- Welcome New York! 🗽✨ We had the best time catching up with the Google team over lunch today. Big thanks to everyone for hosting Markus Vervier and Babette De Decker while they’re in town. #InfoSecCommunity #Networking #Google
- AI agents are transforming how fast we can surface vulnerabilities, but moving fast means nothing if your tools create new safety risks in your environment. As Markus Vervier breaks down in his talk, fully autonomous AI pentesting brings systemic risks; from database destruction to prompt injection and runaway executions. It’s one thing to be aware of these dangers; it’s another to engineer your platform around them. #AIPentesting #OffensiveAI #VulnerabilityManagement
- One of the most powerful and impactful features we did so far: Attack -> Detect -> Improve -> Repeat! You have Nemesis analyze not only the attack, but also IOCs produced by it, then generate detection rules in any common format (Sigma, KQL, you name it)! All automated. Create a full set of custom detection rules in less than 30 minutes and get an instant upgrade to you security defenses.
- If you spend substantial time working on detection rules, this one is for you!
This page shows public professional information only, each fact cited. Is this you? send a correction, or ask for removal within 24 hours, no questions asked.