Overview
Manon Vandebergh is COO of Phished, based in Leuven. She took up that role in June 2024, having joined the company as Head of Operations in June 2021, and she has sat on its board since April 2022.
Before Phished, she worked at Bringme, first as an operations assistant from September 2020 and then as Team Lead HR & Office from March 2021 to May 2022. Earlier she was a legal advisor for start-ups at IusStart between September 2017 and September 2018, and completed an internship as a legal adviser in GDPR and IP at De Juristen - Gent in July 2018. She served as Secretary General of ELSA Leuven from 2016 to 2017 and as its President from 2017 to 2018.
She studied law at KU Leuven from 2013 to 2018, spent 2018 at the Université Toulouse 1 Capitole, and followed a programme in International Management & Strategy at Vlerick Business School from 2019 to 2020.
Career history

In the news
- I sat down with Virginie Claes and Bram Theunis for an episode of the Ondernemerspraat podcast. My angle going in: give companies real, usable tips to actually stop getting hacked. Not theory. Things you can do on Monday morning. Your best employee will click the link. Not because they're careless because the attack was built to fool exactly them with AI. → Why phishing emails are almost impossible to recognize → What phishing emails actually look like today (spoiler alert: nothing like the ones from 6 months ago) → The one habit
- Everyone is talking about AI tools. But I believe the real challenge is something else: 𝗛𝗼𝘄 𝗱𝗼 𝘆𝗼𝘂 𝘁𝗿𝗮𝗻𝘀𝗳𝗼𝗿𝗺 𝗮𝗻 𝗲𝘅𝗶𝘀𝘁𝗶𝗻𝗴 𝗼𝗿𝗴𝗮𝗻𝗶𝘀𝗮𝘁𝗶𝗼𝗻 𝗶𝗻𝘁𝗼 𝗮𝗻 𝗔𝗜-𝗻𝗮𝘁𝗶𝘃𝗲 𝗰𝗼𝗺𝗽𝗮𝗻𝘆? At Phished, we've learned that AI transformation is about much more than technology. It's about mindset, leadership, culture and helping people adapt to a world that is changing faster than ever. The question we continuously ask ourselves is not: "How do we add AI to our business?" But rather: "If we started
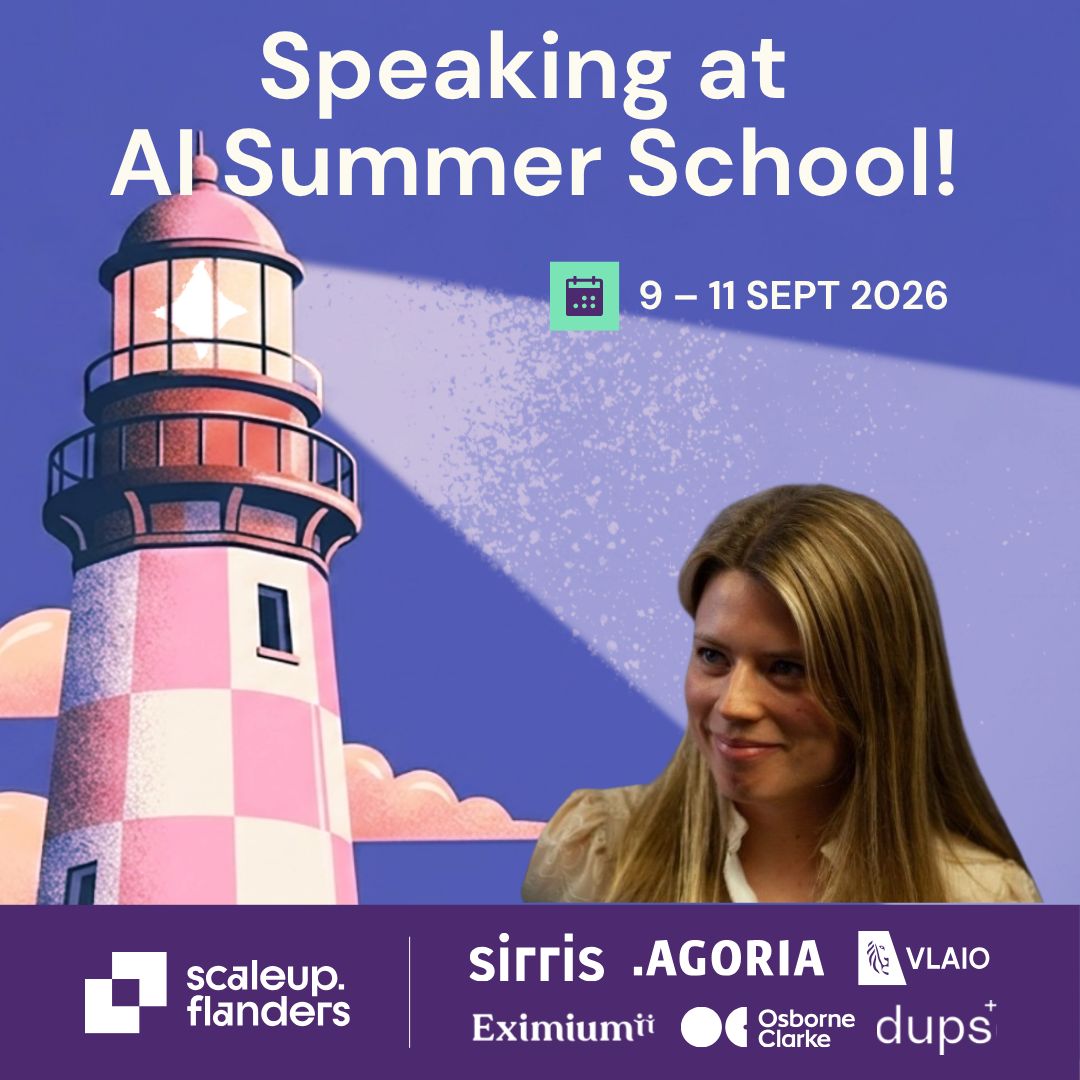
- 𝗪𝗲'𝗿𝗲 Phished 𝘁𝗵𝗲 𝗳𝗶𝗿𝘀𝘁 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗔𝘄𝗮𝗿𝗲𝗻𝗲𝘀𝘀 𝗧𝗿𝗮𝗶𝗻𝗶𝗻𝗴 𝗽𝗹𝗮𝘁𝗳𝗼𝗿𝗺 𝘆𝗼𝘂 𝗰𝗮𝗻 𝗷𝘂𝘀𝘁 𝗿𝘂𝗻 𝗯𝘆 𝗮𝘀𝗸𝗶𝗻𝗴 𝗖𝗹𝗮𝘂𝗱𝗲. So the things you'd normally click through the platform to do, you can now simply ask for in plain language. Want a board-level report? Ask for it. Need to launch a phishing campaign? Ask for it. There are over 90 tools ready to go. No new dashboard to learn. No query language. And because security is what we do, it works strictly within your own permissions.
This page shows public professional information only, each fact cited. Is this you? send a correction, or ask for removal within 24 hours, no questions asked.